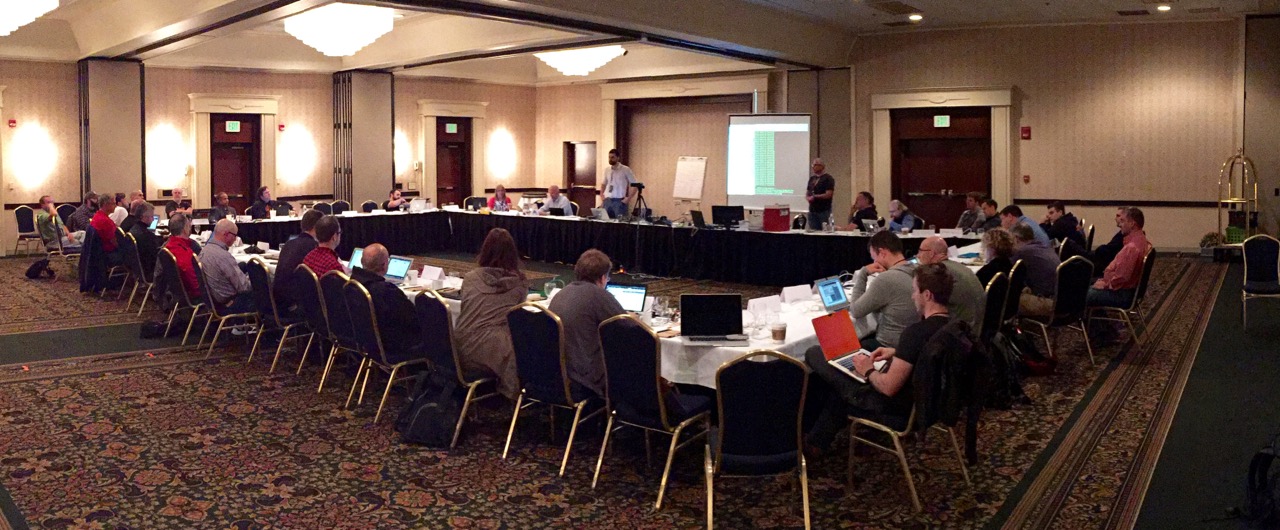
Here’s the first round of TROOPERS16 talks. For more information check out our
website: TROOPERS
Happy Holidays and all the best for 2016 to everybody!
Your TROOPERS Team
===
Mike Ossmann: Rapid Radio Reversing
Wireless security researchers have an unprecedented array of tools at their
disposal today. Although Software Defined Radio (SDR) is the single most
valuable tool for reverse engineering wireless signals, it is sometimes faster
and easier to use other tools for portions of the reverse engineering process.
I’ll discuss how beneficial a hybrid SDR/non-SDR approach has been to security
researchers, and I’ll walk through an example of the process.
In the
first part
of this series we tried to identify which risks related to network-related
threats actually change when IPv6 gets deployed and hence which ones to take
care of in a prioritized manner (as opposed to those which one might be tempted
to [initially] disregard with a “has been there in IPv4 already and we did not
address it then, why now?” stance). Let’s assume we went through this step and,
for those most relevant risks we identified, we want to come up with
infrastructure level controls first, before tackling controls to be deployed on
the host level (as in many organizations the sysowners of “hosts” like servers
in datacenters tend to expect “the network/infrastructure guys to provide the
1st layer of defense against threats”, in particular once those originate from
an apparent network layer protocol, that is IPv6).
We’ve been involved in some activities in this space recently and I thought it
could be a good idea to share a couple of things we’ve discussed & displayed.
Furthermore some time ago – in the
Is IPv6 more Secure than IPv4? Or Less?
post – I announced to come up with (something like) an “IPv6 threats & controls
catalogue” at some point… so here we go: in an upcoming series of a few
blogposts I will lay out some typical elements of an “Enterprise IPv6 Security
Strategy” incl. several technical pieces (and I plan to give a talk on the exact
topic at next year’s
IPv6 Security Summit).
“Welcome to Brazil”, I think, turned to being the most used statement during the
past Hackers to Hackers Conference in Sao Paulo. It was used as the main
reaction to every speech taking moment, and there were a lot of those! To honor
the moments and give you a quick insight into was what going on in Sao Paulo,
here is a quick summary of the overall event and our own contribution.
we (Christopher, Jan-Pascal and me) had the pleasure to join the 7th
DENOG (German Network Operators
Group) meeting in Darmstadt
which takes place yearly in autumn. For the first time the meeting was scheduled
for two days which offered more time for talks and discussions than the previous
meetings. The concept of DENOG is to meet, talk, discuss and share experience
with the network operator community in Germany.
The meeting started withe a talk from Peter Sievers from Juniper about Network
Automation and Programmability. He presented why automation and programmability
is getting more and more important even for network operators. It will help to
automate the build process, the configuration and should ideally help you
operating and troubleshooting your envirnoment. The focus of the talk was on the
platforms which are already available and ready to use to automate day to day
activities.
Last week I had the pleasure to attend the “escar” (Embedded Security in
Cars) conference in Cologne, Germany.
Arriving late Tuesday, I had the chance to get a rich breakfast before joining
the con in the hotel Dorint at Cologne’s famous place the Heumarkt.
Unfortunately I had to deal with two stumbling blocks on my way to the Dobrint:
The magnetic sensor of my mobile which went crazy (no compass) and – the date.
11th of November in Cologne means just one thing – carneval! The whole
city was just in a state of exception. Everybody on my way to the venue seemed
to be drinking or beeing already drunk – at 9am! 😉
Being a little late, I went straight to the room after registration. As there
was only one track to follow you could not miss any talk – nice thing!
After we were welcomed by the hosts, and the first talk started.
Last week, on the 27th-28th I attended a nice wireless conference in berlin, the
WLPC (Wireless LAN Pros Conference). You can visit their website at
http://berlin2015.wlanprosconference.com.
This conference is a community-driven conference from wireless professionals
with focus on typical topics that come up when you are planning or running large
wireless networks. This is a mainly Twitter based community, you can see some
Tweets with hashtags #WLPC for example. There were also some interesting talks
about future networks, for example Marko Tisler gave a talk about wireless LAN
and SDN and what we can expect and what SDN will not solve for wireless
networks.
In mid-October our friend Bryan Fite aka Angus Blitter invited the community for
the ninth edition of Day-Con. Bryan’s annual security
summit, which we regard as the sister event of TROOPERS, is a pretty good reason
to visit lovely Dayton, Ohio.
And so we did… ERNW sent in five delegates. Delegates is Day-Con-speak for all
attendees and speakers and such a subtle choice of wording sets the tone for the
whole event. People seemed to be really focused and the
roundtable-like setting during the talks (see above) provided a cozy atmosphere
for in-depth expert chatting.
That was the opener for my presentation on the Security in Medical Devices at
CodeBlue 2015 last week in Tokyo, Japan. A
Code Blue
often describes a patient in a critical condition, mostly needing resuscitation.
That just seemed to be a perfect match, also in the sense that the condition of
some medical devices out there are still pretty critical concerning security. If
you follow our current research on this you know what I am talking about. I hope
that we are not talking about this topic anymore three years from now. That
would mean that we have made the world a safer place, although it took some time
… 😉
Some readers will probably be aware that we are amongst the proponents of a
quite strict stance when it comes to filtering IPv6 packets with (certain)
Extension Headers and/or fragmentation, because those can be the source of many
security problems (as laid out
here,
here
or
here).
Actually I still think it was a very good idea of, amongst others, Randy Bush
and Ron Bonica to
suggest the deprecation of IPv6 fragmentation in the IETF.
On
the other hand there are voices arguing that fragmented IPv6 packets will be
needed in some cases, namely DNS[SEC]-related ones.
In this post I will discuss some details of this debate (taking place in many
circles, incl.
this thread
on the ipv6-hackers mailing list which, btw,
you should subscribe to).