In mid-October our friend Bryan Fite aka Angus Blitter invited the community for
the ninth edition of Day-Con. Bryan’s annual security
summit, which we regard as the sister event of TROOPERS, is a pretty good reason
to visit lovely Dayton, Ohio.
And so we did… ERNW sent in five delegates. Delegates is Day-Con-speak for all
attendees and speakers and such a subtle choice of wording sets the tone for the
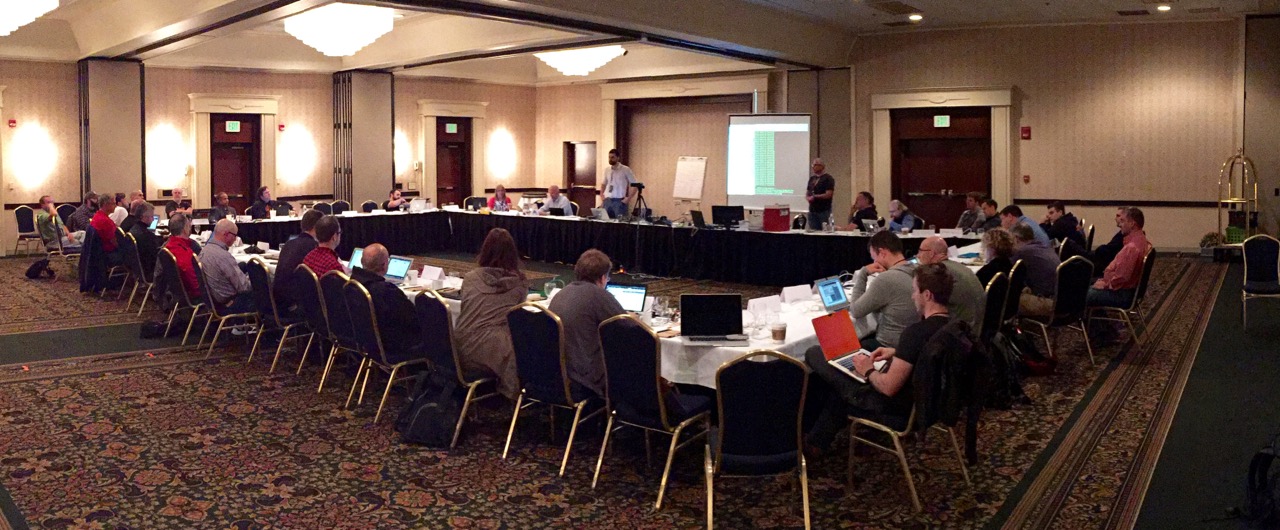
whole event. People seemed to be really focused and the
roundtable-like setting during the talks (see above) provided a cozy atmosphere
for in-depth expert chatting.
That was the opener for my presentation on the Security in Medical Devices at
CodeBlue 2015 last week in Tokyo, Japan. A
Code Blue
often describes a patient in a critical condition, mostly needing resuscitation.
That just seemed to be a perfect match, also in the sense that the condition of
some medical devices out there are still pretty critical concerning security. If
you follow our current research on this you know what I am talking about. I hope
that we are not talking about this topic anymore three years from now. That
would mean that we have made the world a safer place, although it took some time
… 😉
Some readers will probably be aware that we are amongst the proponents of a
quite strict stance when it comes to filtering IPv6 packets with (certain)
Extension Headers and/or fragmentation, because those can be the source of many
security problems (as laid out
here,
here
or
here).
Actually I still think it was a very good idea of, amongst others, Randy Bush
and Ron Bonica to
suggest the deprecation of IPv6 fragmentation in the IETF.
On
the other hand there are voices arguing that fragmented IPv6 packets will be
needed in some cases, namely DNS[SEC]-related ones.
In this post I will discuss some details of this debate (taking place in many
circles, incl.
this thread
on the ipv6-hackers mailing list which, btw,
you should subscribe to).
The current trend of social coding finally arrived at ERNW! From now on, you
will find our public released tools and scripts commonly
on https://github.com/ernw. Therefore I would like to
share some thoughts/guidelines which you have to keep in mind if you want to be
a social coder:
Github and other repository hosts are great if you want to share opensource
tools with the community, as they will find a common platform with defined
workflows to extend/fix the work to get better software for everyone. What some
should note is that (especially in terms of decentralized version control
systems (DVCSs) like git, bazaar or mercurial) public really means public. Back
in earlier days, if you shared your code with others you probably created a
source code package of a defined version of your code. They will get the files
you published, nothing more (and nothing less). Beginning with websites like
sourceforge, a broader range of public VCSs came up (mostly driven by CVS or
SVN). At this time, others were able to view your commit history (if you granted
access to them) and all your mistakes you’ve done before your published code
state (for example accidentally committed sensitive data). Those mistakes can
still happen today. The difference with the DVCS used nowadays is that most of
the time you have lesser control of your commit history (in the same way if
someone had copied your history commit by commit in SVN, but then you may had
noticed it because of the high network traffic). With DVCS, everyone gets a full
copy (clone) of your repository even on a simple “checkout” (as called in SVN).
This means he/she is able to search your history locally and has all the time
he/she needs to do it. Even if you delete your repository (or modify the
history), the original state is shared over all who have cloned it beforehand
(thats one reason why DMCA takedowns are not that powerful/useful against git
repositories). Most of the public hosting platforms even included a search over
all repositories (which is really useful if you want to find some tool or try to
find the reason why a local tool doesn’t work).
today we want to share a method on how to test an OCSP over HTTP validation
service with Burp and some Python magic. First a little background about OCSP
(Online Certificate Status Protocol): the main purpose of OCSP is to validate
the status of an X.509 certificate.
The OCSP responder is the key part of the system. It is run by the certificate
authority and responds with one of three possible different answers. The first
one is “good”, which indicates that the certificate is not banned, “revoked”
means that the certificate is banned, and “unknown” simply says that the status
could not be determined, because the issuing CA of the Cert is not known to the
responder.
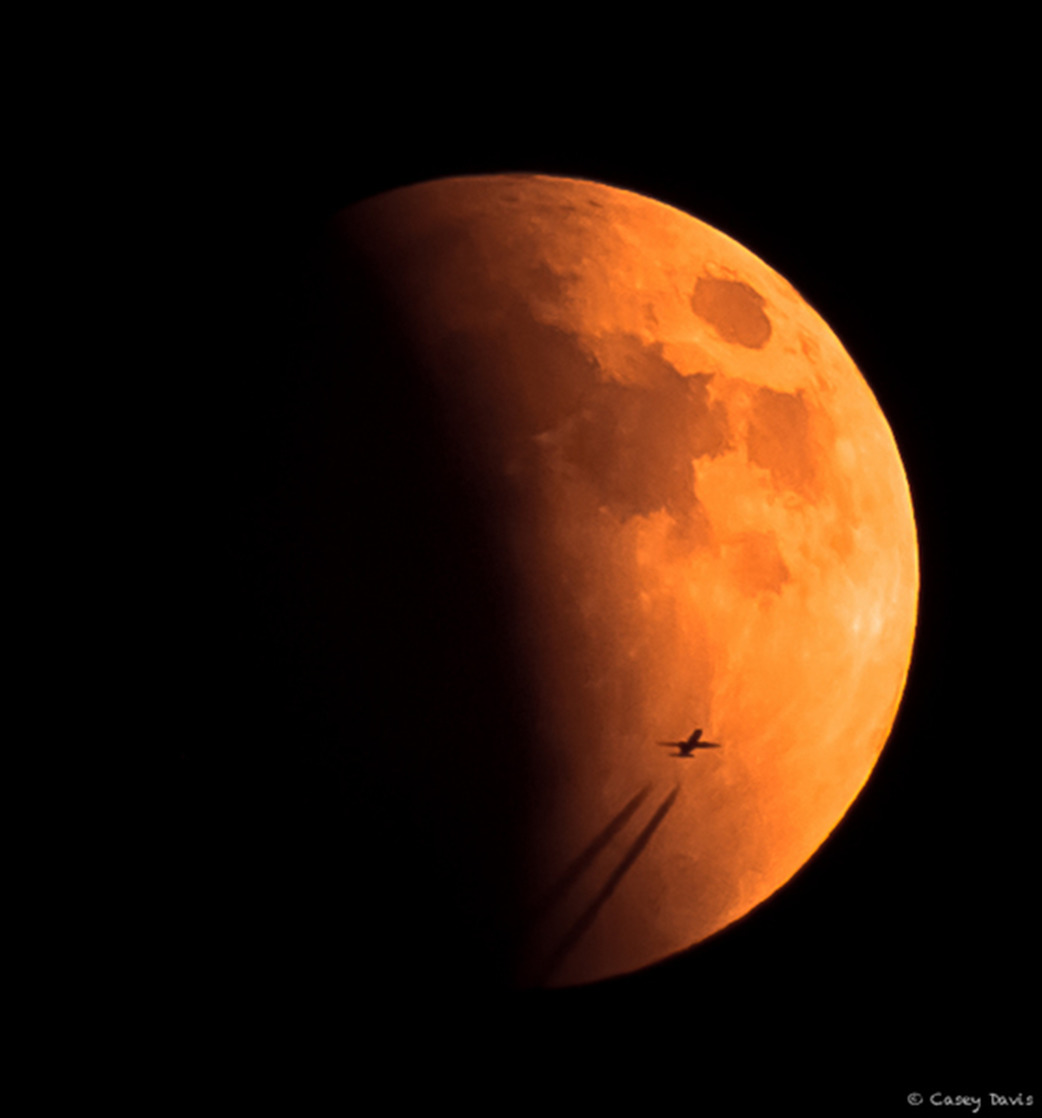
On Monday the 28th of September 2015 a rather rare event occurred. At around 4
a.m. the moon changed its colour into a dim of red, luckily the sky was clear
enough to see something.
If you missed that event your next chance will be in about 15 years or so.
The reason for being awake this early wasn’t the moon in the first place but
what followed afterwards – my trip to the
hardwear.io Security Conference in The Hague.
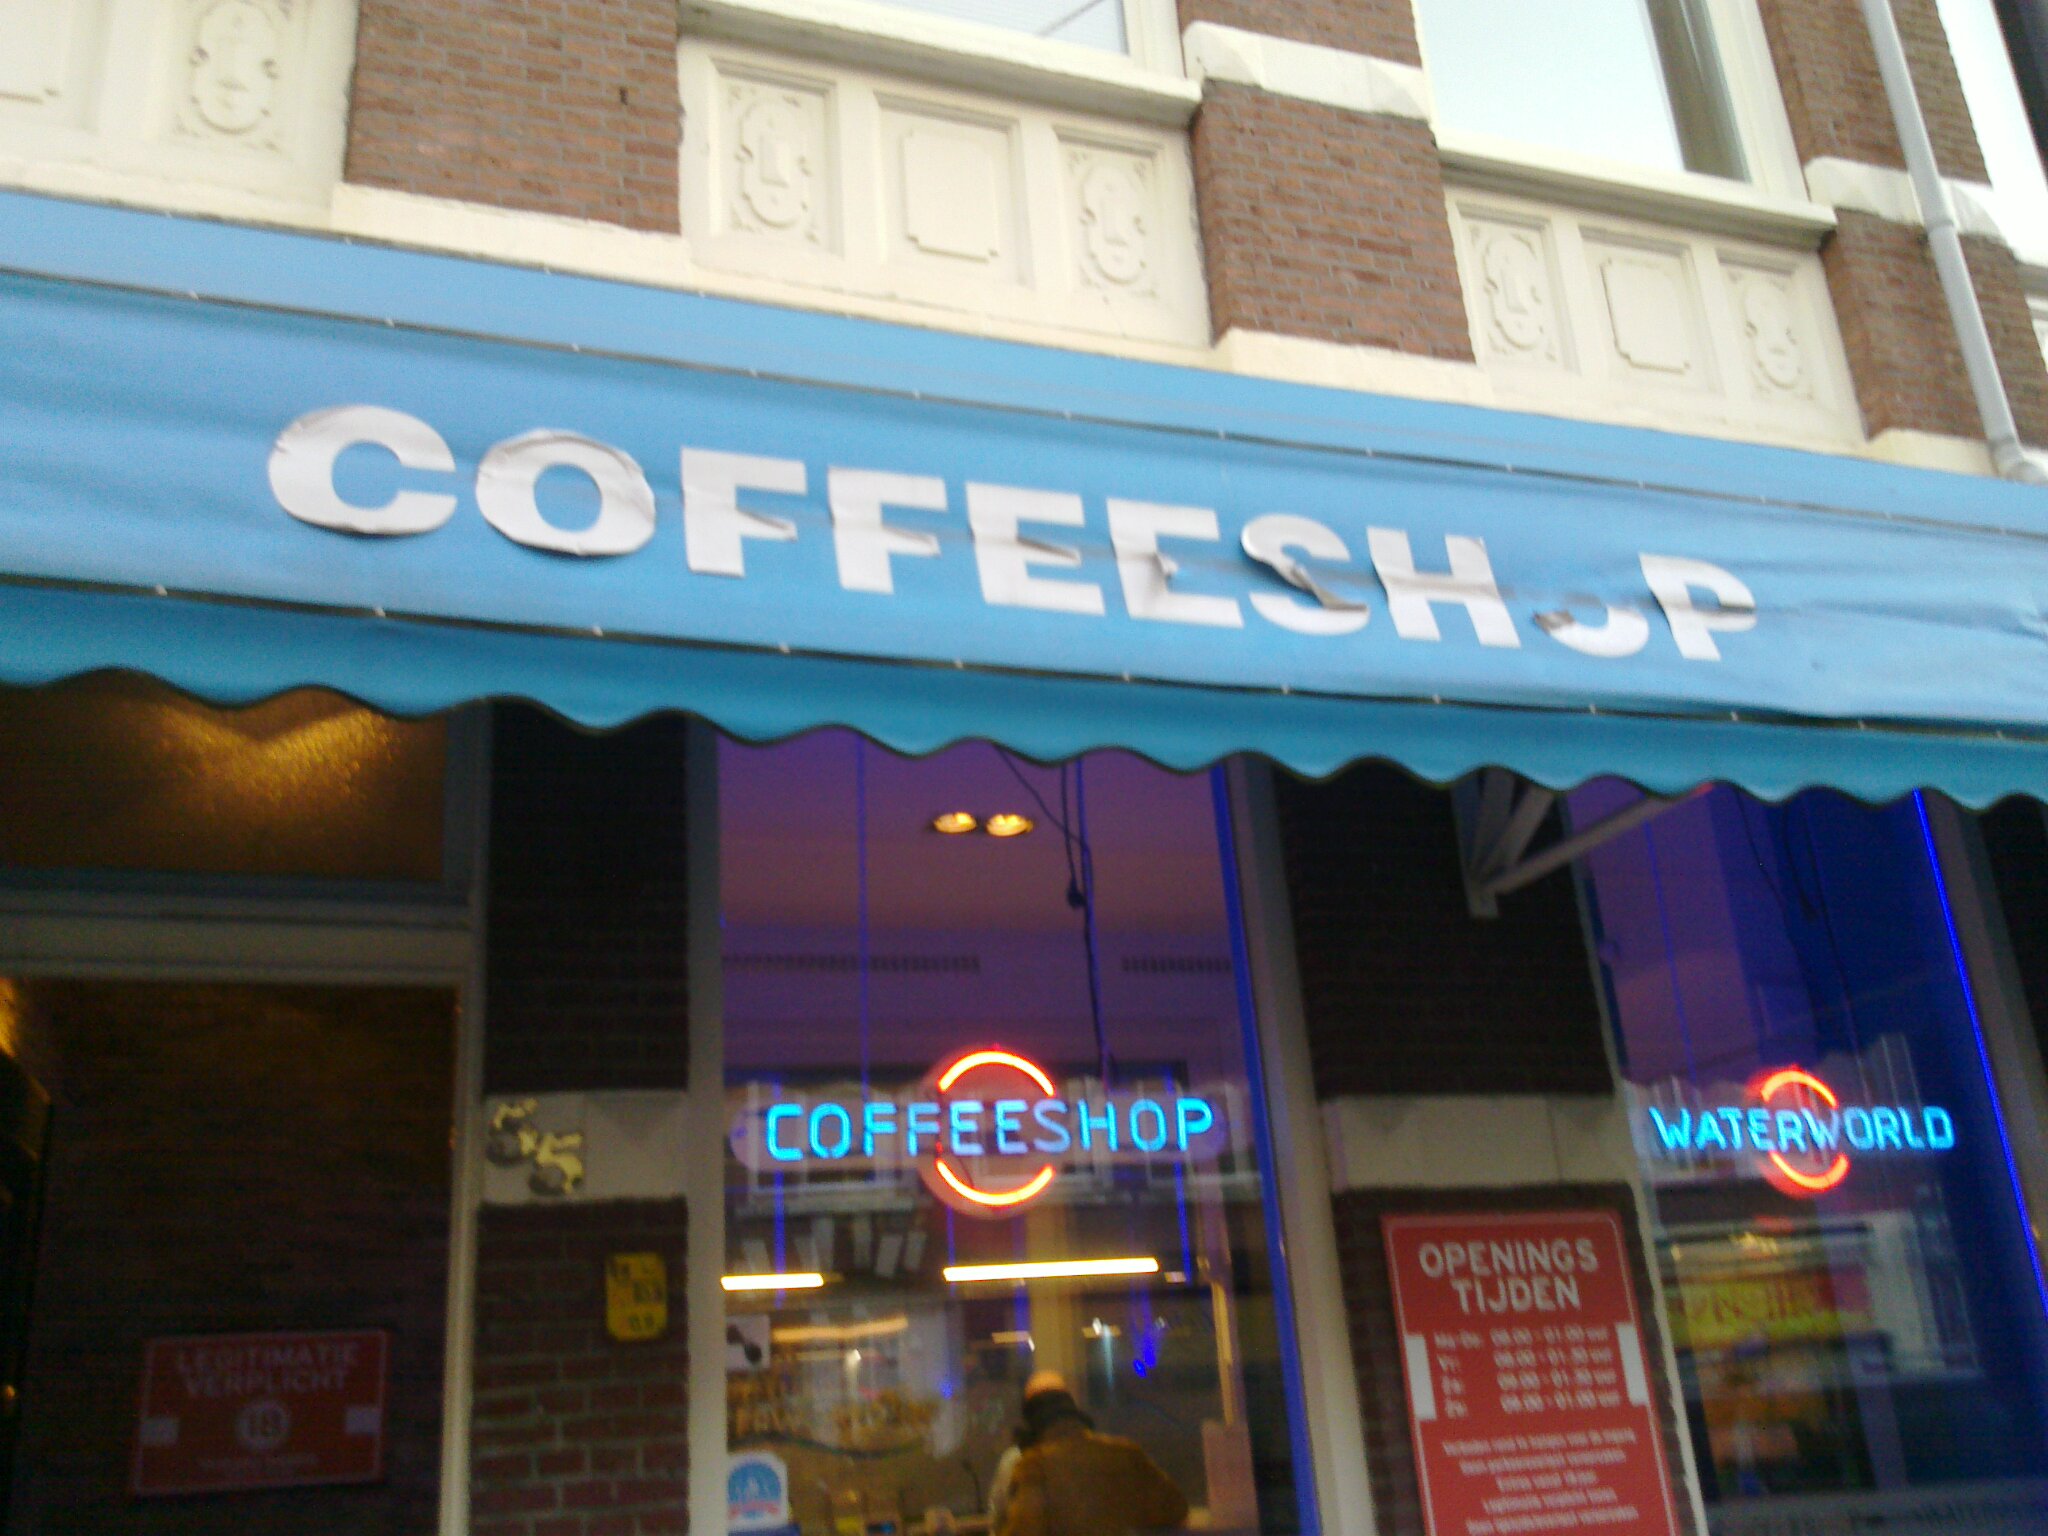
During my stay in The Hague I needed to print something, so I asked for a Copy
shop and this is where they sent me:
Against the common rule to just talk about the personal favorites, I will cover
all talks in one, two or more sentences (arbitrarily decided while
writing). This also gives you a broader picture of the conference.
Jumping right in with the keynote of Day 1 by Jon Callas and my favorite quote
“Make your devices fixable”. Enough said.
Unlike the German Oktoberfest in Munich which already started in September, the
Oktoberfest in The Hague started on 2nd October.
In spite of this competing event the decision going to the last day of the
hardwear.io Conference definitely paid off.
Day 2 started with the Keynote from Harald Welte (the father of Osmocom) and his
view about Telecom Security for the last few years. His observation is that
nothing has changed so far – we still suffer from a lack of tools and
monoculture throughout the industry.
On October 1st and 2nd Flo and I were presenting at
hardwear.io in The Hague, NL. My topic was
“Living in a fool’s wireless-secured paradise”
and Flo was presenting his current research
on medical device security. It was the first talk at an international
security conference for me and I am still quite excited!
I was speaking about the (in)security of wireless consumer alarm
systems, which you can buy just in every consumer electronics store
around the corner for about $10 – $250. I analyzed the systems on
different levels, e.g. looking at UART and JTAG and the wireless domain
with Software Defined Radio (SDR). I gave an overview of my current
research and the tools I usually use for hardware hacking, especially my
favorite thing to play with: SDR.
Last week Christopher and I were the instructors of
an IPv6 workshop.
In this one we usually build a lab with the participants incl. a variety of
routed segments and native IPv6 Internet access. Once the latter part is
implemented people start poking around and surfing the Internet from their
laptops, not least to find out which sites they can actually reach from an
v6-only network (please note that
actually there are many).