Last week Christopher and I were the instructors of an IPv6 workshop. In this one we usually build a lab with the participants incl. a variety of routed segments and native IPv6 Internet access. Once the latter part is implemented people start poking around and surfing the Internet from their laptops, not least to find out which sites they can actually reach from an v6-only network (please note that actually there are many).
Continue reading Continue readingBeing at VB2015…
I am currently at the 25th Virus Bulletin International Conference in Prague. The VB2015 is hosted by the Virus Bulletin portal and provides three full days of learning opportunities and networking.
VB2015 focuses on the key themes:
-
Malware & botnets
-
Anti-malware tools & techniques
-
Mobile devices
-
Hacking & vulnerabilities
-
Spam & social networks
-
Network security
General Observations:
What I liked about VB2015 was the very friendly and always helpful staff. The good conference location, it never felt overcrowded or to empty and the very good catering during the conference.
Continue reading Continue readingVMware did it again: vCenter Remote Code Execution
Yesterday 7Elements released the description of a Remote Code Execution vulnerability in VMware vCenter. The information came in at a good point as I’m at the moment drafting a follow-up blogpost for this one which will summarize some of our approaches to virtualization security. The vCenter vulnerability is both quite critical and particularly interesting in several ways:
- Once there is proper network isolation & restriction, the vulnerability should not be exploitable from the overall corporate network (or maybe even the Internet — a quick inaccurate shodan search for “vcenter” returned about 1800 results and at random checks actually revealed vCenter systems). It should also not be exploitable from ESXi hosts managed through the vCenter: ESXi hosts need to be able to connect to the vCenter for heartbeat messages, however “only” on ports 443 and 902 — the vulnerability exploits a service running on TCP ports 9875 – 9877.
- It is questionable whether the exploited Java RMI functionality is really required for the operation of VMware infrastructures. This blogpost provides further detail on the known type of vulnerability in Java applications. VMware had a similar issue back in 2010, where their workaround to fix a vulnerability was to just disable the affected component, resulting in the impression that it wasn’t even required in the first place. Let’s see whether the future will bring up more vulnerabilities which could have been prevented by implementing more thorough hardening of all components (e.g. following the minimal machine principle). Furthermore in 2011 there was a similar 3^(rd) party component vulnerability in vCenter which we covered in this blogpost. The totality of our posts on VMware security can be found here.
- For high-security environments we have been recommending for some time to use a dedicated vCenter per hypervisor cluster (i.e. if you have two hypervisor clusters, one for internal and one for DMZ systems, you should use two separate vCenter systems). Vulnerabilities like these illustrate the need for that, given that the ESXi hosts need to be able to access the vCenter on the network level.
Happy patching & stay tuned,
Continue reading Continue readingBlackHoodie: Reversing Workshop for Women
In the beginning of September, I had an opportunity to take part in BlackHoodie – a reversing workshop for women organized by Marion Marschalek, senior malware researcher at Cyphort, Inc. It took place on 5th and 6th of September at University of Applied Sciences St. Pölten, Austria.
Besides me, 14 more young women from different countries came to attend the workshop; the overall atmosphere was very friendly and productive. Before the actual event all participants were getting preparatory assignments and recommendations (not to spend our two days on learning the very basics), and during the workshop itself we got our hands on analyzing and reversing some actual malware samples. I personally found it very interesting how one can detect and overcome several layers of anti-analysis protection. I left the workshop excited and packed with some new knowledge as a basis for further skills development – it’s just the beginning! 😉
Continue reading Continue readingPython For Hackers
Python has reached a defacto standard in exploit development lifecycles and most of the proof of concept tools you’ll find out there are written in Python (besides the metasploit framework, which is written in Ruby). Python allows to write scripts handling with remote services, fiddling with binary data and interacting with C libraries (or Java in case of Jython/.Net in IronPython) in a fast and easy way. The huge standard library with it’s “battery included” principle removes some of the dependency hell known from other frameworks/languages. I want to share some of my python coding experiences with you, and maybe this could give some helpful tips for your future work, to make the world a bit safer 🙂 (PS: most of the examples are written in Python 3.x or compatible to both Python branches).
Continue reading Continue readingNew iOS Version – New Lockscreen Bypass
At the 16th of September Apple released its new version of the mobile operating system iOS 9. As several versions before, this new iteration suffers from a weakness that makes it possible to bypass the lockscreen without entering the respective PIN code. Exploiting this flaw requires Siri to be enabled and phyiscal access to the phone. A successful exploitation results in a major loss of confidentiality as all photos and contacts in the phonebook can be accessed by the attacker. The following steps lead to the lockscreen bypass:
Continue reading Continue readingReminiscing About Black Hat USA 2015
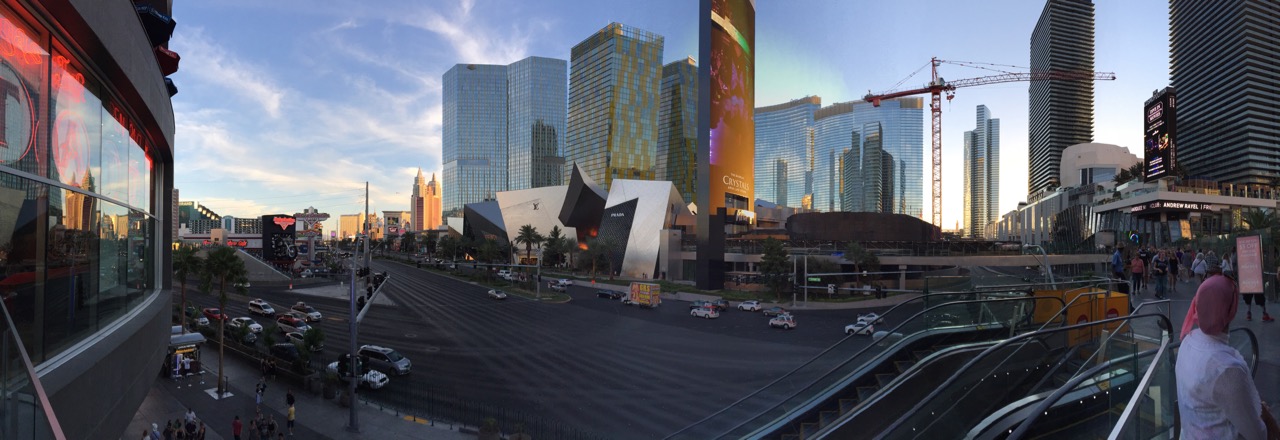
While searching for some photos for my last blog post on Thinkst Canary I found a couple more from our recent trip to Black Hat USA and DEF CON, which I consider worth sharing. Nothing too technical, just some visual impressions and comments from my side. Let’s get it on!
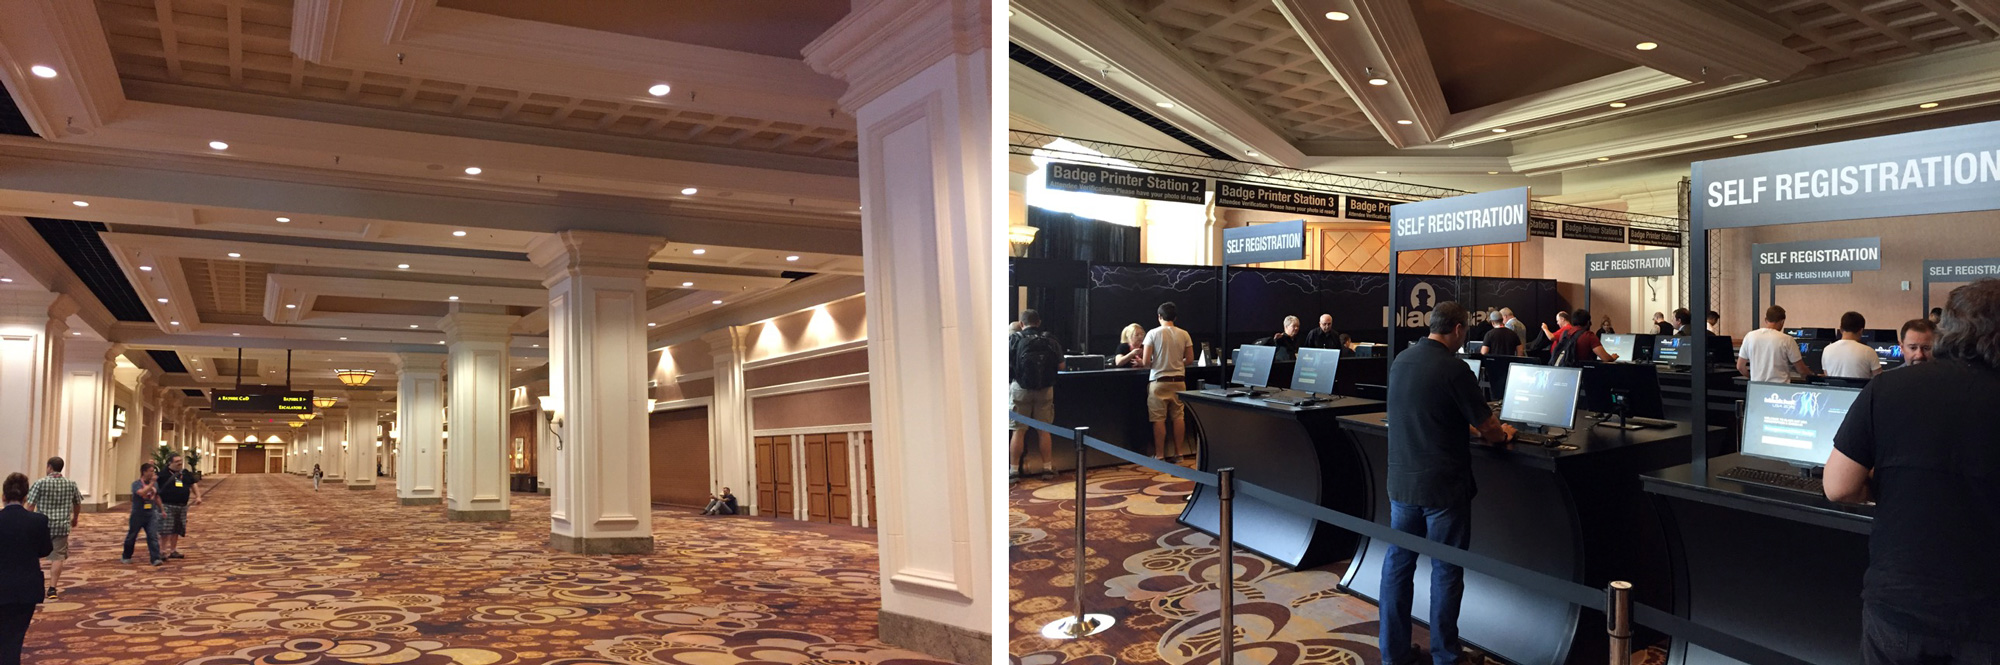
My colleague Patrik and myself arrived one day early before the briefings and headed right to Mandalay Bay to check out the Black Hat venue and get a feel for the city. The sheer size of just everything is mind-blowing.
Continue reading Continue readingMiner’s Canary Revival in IT Security
What is a Miner’s Canary?
Well, it’s a canary (these cute yellow songbirds some people have as a pet), and its main feature is that it dies before you will.
What the hack [pun intended]? And by the way… what has this to do with IT Security? Well… let me first quote Wikipedia on the birds:
“Canaries were once regularly used in coal mining as an early warning system. Toxic gases such as carbon monoxide, methane or carbon dioxide in the mine would kill the bird before affecting the miners. Signs of distress from the bird indicated to the miners that conditions were unsafe.” Source: https://en.wikipedia.org/wiki/Domestic_canary#Miner.27s_canary
Continue reading Continue reading
IPv6@MRMCD2015
Greetings everyone,
On Saturday last week I had the pleasure of delivering a workshop on IPv6 networking at the MRMCD2015 conference in Darmstadt, Germany. It goes without saying that the atmosphere was quite amicable; as usual at CCC-related events. What definitely impressed me the most was the diversity of the audience. There were around thirty attendees representing several age groups and all with seemingly differing backgrounds.
The engagement of everyone was stunning. I questioned the most engaged attendees relentlessly and they fired back. I was being constantly bombarded with questions from enthusiastic geeks and they got, hopefully, what they deserved. This provided for a great learning environment, a friendly atmosphere and in my humble opinion really constructive dialogues. Well, one has to be interested and enthusiastic in order to spend three hours on a rainy Saturday evening discussing IPv6.
Continue reading Continue readingSending Mixed Signals – What Can Happen in the Course of Vulnerability Disclosure
Update:
Given there’s quite some speculation and, as we think, misinformation going around we think it’s helpful to add/clarify the following information:
- we fully comply with the injunction and we have no intentions to violate it. we do not plan to publish any technical information besides the report (agreed upon with FireEye themselves) and the slides (based on the former) anyway. No 3rd parties except for the ones involved (FireEye, lawyers) have received any additional technical information from our side, let alone an earlier version of the report.
- the injunction covers accompanying details mostly within the architecture space, but not the core vulnerabilities themselves. Those are not part of the injunction.
- we stand by the timeline as provided below. In particular, the following two
points:
– FireEye received a draft version of the report which had the objectionable material (as identified by the cease and desist letter) fully removed on August 11th.
– according to the cease and desist letter FireEye’s lawyer sent us, they were informed – from our side – about the planned talk at 44CON on Jul 23rd. - there’s an injunction, but not a lawsuit. I used the term “sue” after consulting Merriam-Webster which states: “sue: to seek justice or right from (a person) by legal process”, but this might have been misinterpreted by some readers. As stated, there’s a pending injunction, but not a lawsuit.
Please note that we won’t share legal documents with 3rd parties or publish them
as we consider this inappropriate.
Please note further that, during the whole process, our goal was to perform a
responsible disclosure procedure with its inherent objectives (namely
vulnerability remediation by vendor and education of various stakeholders
involved, see also
here
or
here).
We consider this disclosure process as concluded. We don’t see a need to add
technical details from our side as we feel that the objectives of responsible
disclosure are met (not least as patches are released since quite some time
and both
vendor & finder
have released reports).