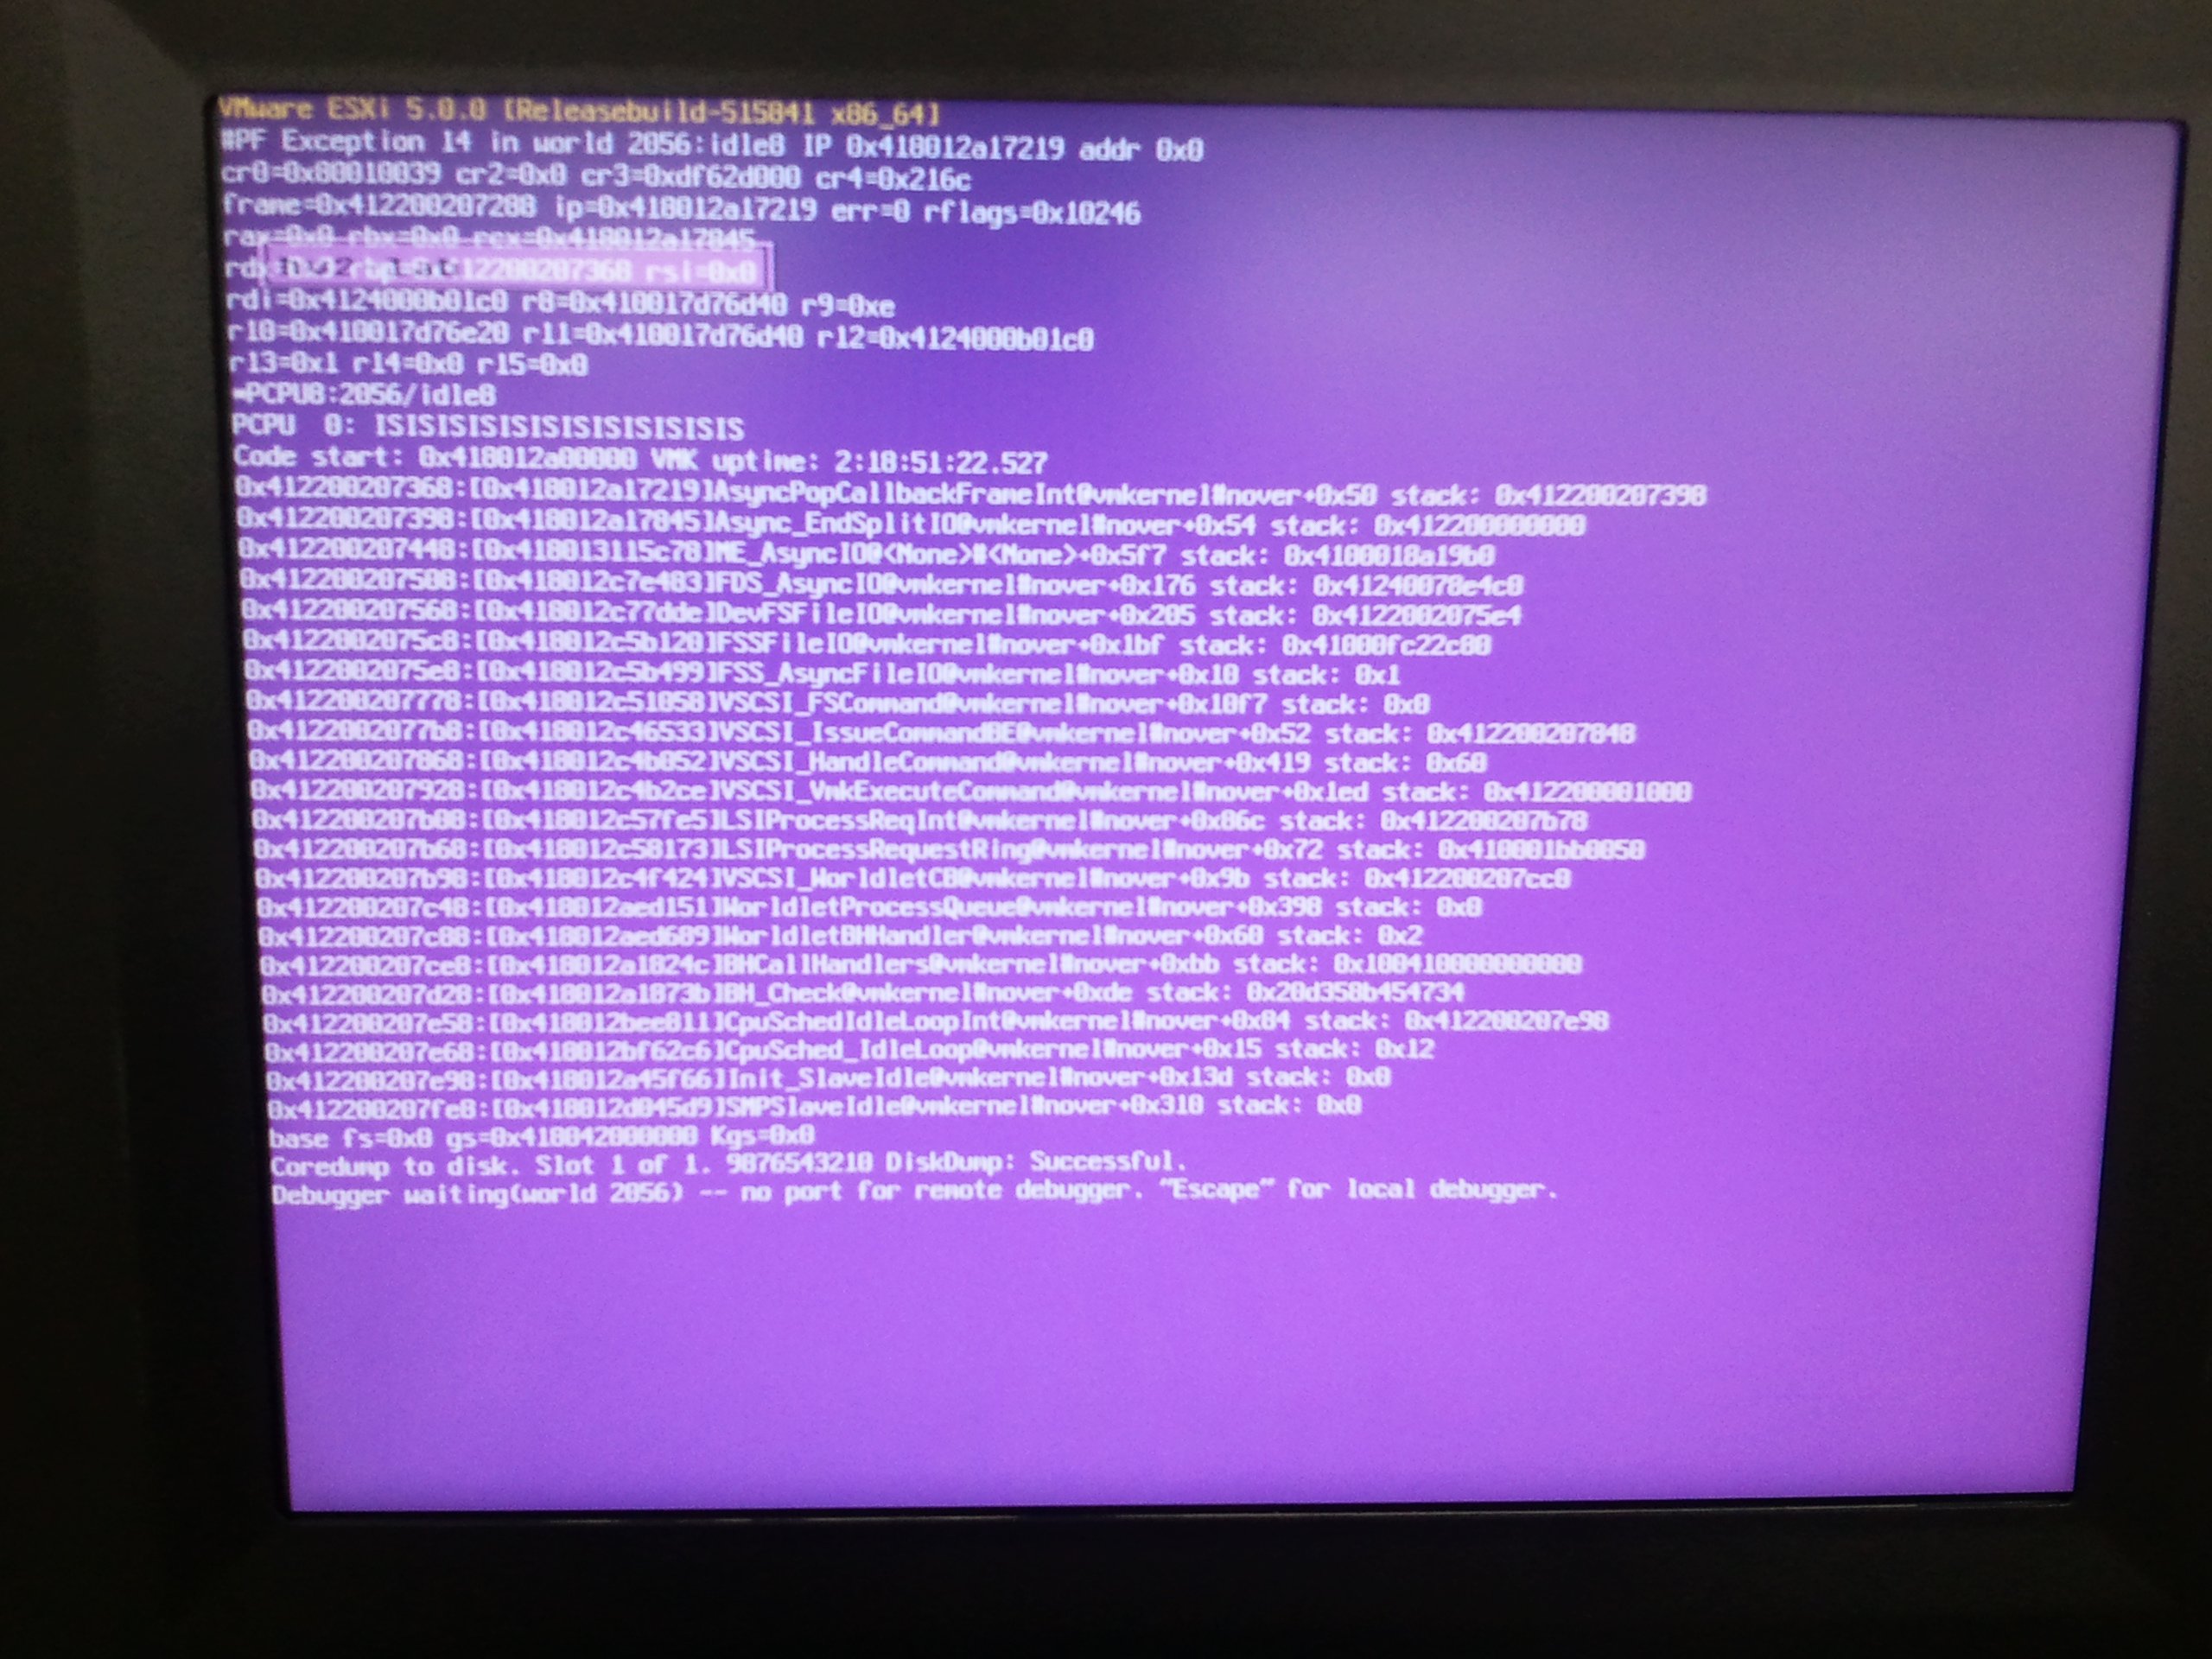
Almost all of our presentations and write-ups on the VMDK File Inclusion
Vulnerability contained a slide stating something like
“we’re rather sure that DoS is possible as well ;-)”
including the following screenshot of the ESX purple screen of death:
So it seems like we still owe you that one — sorry for the delay! However the
actual attack to trigger this purple screen was rather simple: Just include
multiple VMDK raw files that cannot be aligned with 512 Byte blocks — e.g.
several files of 512 * X + [0 < Y < 512] Bytes. Writing to a virtual hard
drive composed of such single files for a short amount of time (typically one to
three minutes, this is what we observed in our lab) triggered the purple screen
on both ESXi4 and ESXi5 — at least for a patch level earlier than
Releasebuild-515841/March 2012: it seems like this vulnerability was patched in
Patch
ESXi500-201203201-UG.
Two weeks ago we had a great time at
Day-Con VI. Enno, Matthias, Rene, Frank and
me traveled to Dayton, OH to give workshops and presentations. We started a
tough week full of workshops on Tuesday where
Rene gave a deep inside look into the world of security on current mobile
platforms. Matthias discussed security problems and possible design patterns of
cloud environments in his Cloud & Virtualization Security Workshop before he
gave a first insight into the world of reverse engineering on Wednesday. Frank
and me taught the basics of hacking and pentesting in the
PacketWars bootcamp (comparable to the one at
TROOPERS),
preparing the participants for the
PacketWars on Saturday. Obviously we were
not the only ones having a
great time
😉
pytacle is a tool inspired
by
tentacle.
It automates the task of sniffing GSM frames of the air, extracting the key
exchange, feeding kraken with the key
material and finally decode/decrypt the voice data. All You need is a
USRP (or similar) to capture the GSM band and a
kraken instance with the
berlin tables (only
about 2TB 😉 )
I’ve posted a preview
before, take a look at the video to see the tool in action.
Microsoft takes this vulnerability quite serious and was acting fast. The
Microsoft Security Response Center announced the availability of a fix last
night in the
MSRC Blog.
The fix will be available via Windows Update on friday, the 21st of september.
So it’s time to get ready for this update ;-).
Actually a Windows Vulnerability
(Microsoft Advisory 2757760) related
to the Internet Explorer Version 7, 8 and 9 is in the news. Microsoft is aware
of the problem, but there’s no patch available yet. We call this a 0-Day :-).
Making the problem even worse, on monday reliable
exploit code
was released within the Metasploit project, so exploit code is already in the
wild.
Disabling Active X and Active Scripting in the Internet Settings
But both of them have some impact: EMET must be deployed before any usage (btw.
EMET can be configured via Group Policies) and disabling Active X and Active
Scripting might break some business relevant web sites (that can be added to the
“Trusted Sites” Zone, but might produce major operational effort).
In our last series of posts regarding the VMDK file inclusion attack, we focused
on read access
and
prerequisites
for the attack, but avoided stating too much about potential write access. But
as we promised to cover write access in the course of our future research, the
following post will describe our latest research results.
First of all, the same
prerequisites
(which will be refined a little bit more later on) as for read access must be
fulfilled and the same
steps have to
be performed in order to carry out the attack successfully. If that is the case,
there are several POIs (Partitions Of Interest) on a ESXi hypervisor that are
interesting to include:
Recommendations by the
German Federal Office for Information Security
(BSI – Bundesamt für Sicherheit in der Informationstechnik) are obligatory for
German government agencies, civil services and authorities (like recommendations
of the NIST are relevant to American government agencies and authorities). They
are often used as references and security best practices in other countries as
well. Hence it is hard to understand why the recommendations on how to harden
Windows Server 2008 based systems were published only some weeks ago and
only on a preliminary draft basis (which is, obviously, better than nothing
;-)).
Last week I read about the new networking features of the integrated vSwitch of
Hyper-V 3.0. I was quite surprised that RA Guard will be natively supported and
was curious about implementation and functionality. If you don’t know how RA
Guard works, I recommend reading our previous blog posts
here,
here,
here,
here
and
here,
or have a look at our workshop at
Troopers12.
I downloaded Windows Server 2012 RC to do some practical testing. Since my
girlfriend was working the whole weekend, I had plenty of time to play around
with all that stuff without risking trouble 😉
As every year, we
will be attending Day-Con, a one-day security summit in
Dayton, OH — this year for its VIth edition. Even though the actual conference
comprises “only” one day full with talks and discussions (please find the agenda
here), the overall event
consists of trainings before the conference
and PacketWars battles (including an infamous party)
afterwards. Since we will be leading and attending some of the training
sessions, those might be of particular interest for people who missed our
Troopers workshops — so
you don’t have to wait a whole year but get another chance in October 😉
Some days ago another
advisory
related to a web application firewall (WAF) product was published. This time the
product Airlock by Ergon was affected by a vulnerability
that combines Encoding and NULL Byte attacks to circumvent the pattern based
detection engine. We have described these attacks in detail in our newsletter
“Web Application Firewall Security and The Swiss Army Knife for Web Application Firewalls”
because they belong to a well known category of attacks against WAFs.