The HITBSecConf or “Hack In The Box” in Amsterdam is a well known security
conference in Europe. We also attended this year too, and there were quite some
interesting talks at the HITBSecConf16 conference. One of the talks was about
“New Methods for Exploiting ORM Injections in Java Applications” by the security
researchers Mikhail Egorov and Sergey Soldatov.
I. What is Object-Relational Mapping (ORM)?
ORM stands for Object-Relational Mapping, which is a technique that
automatically converts data from a relational database management system (RDBMS)
into objects. This is often used in business applications of today.
Last week we have visited the HITBSecConf16 – conference in Amsterdam.
There were many interesting talks, and in this post I am going to tell you about
a talk held by Radu Caragea – “Telescope: Peering Into the Depths of TLS Traffic
in Real-Time”.
While performing a dynamic malware analysis one often needs to analyze network
traffic in order to determine malware communication with C&C servers, to observe
the malware delivery from sites, or to investigate honeypot traffic under TLS.
There are already existing solutions to help with this task. However in the
given talk considering virtual environments the speaker presented a novel
technique that works for virtualized machines with a minimal overhead, and is
actually OS-agnostic and crypto-library-agnostic.
Last week we enjoyed quite a wonderful HAXPO exhibition and HITB conference in
Amsterdam. A number of great talks could be heard at the main HITB conference
such as “Bootkit via SMS: 4G Access Level Security Assessment” or
“Stegosploit: Hacking with Pictures“. And not only that: there were also
several engaging hands-on workshops.
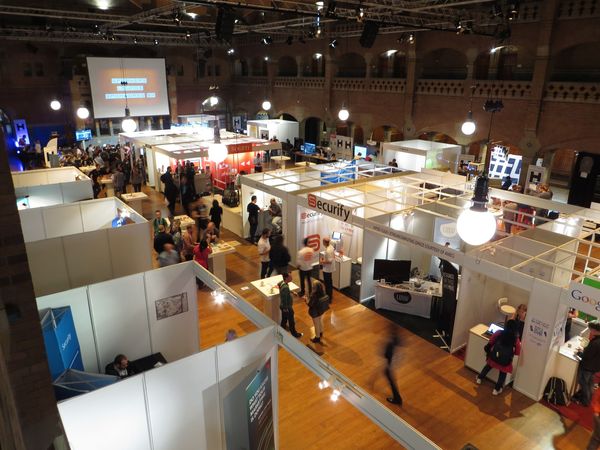
Apart from the main conference, there was the HAXPO – a hacker exhibition. At
this exhibition you could connect with people from different companies, get a
lot of merchandise, and also listen to several briefings on security and its
philosophy. Fortunately, we had the pleasure to present two of these briefings
and maybe you tested your web application skills at the ERNW booth.
There are lots of interesting places to visit in Amsterdam, but if you are there
between the 26th and the 29th of May, then our booth at HAXPO exhibition should
be your main destination.
HAXPO is a great exhibition, where you can
become up-to-date with the latest security technologies, attend various
workshops and get in touch with more than 35 IT and information security
companies. It will take place in the beautiful historical building “Beurs van
Berlage” in the center of Amsterdam. As usual, ERNW will take part in HAXPO. We
will be waiting for you in the Community Village section (booth NL-018). Come
visit and get to know more about us. You are invited to take our hacking
challenges, where the levels of complexity vary from beginners to advanced.
Furthermore, we will bring our KNX hacking suitcase!
Past month we (which is me and a group of other ERNW students, supported by some
of the “old” guys — I hope my team lead won’t yell at me for this 😉 ) attended
the Haxpo and Hack in the Box in Amsterdam. Starting from 28. May, we had three
days at this great conference (HITB) and exposition
(Haxpo). The two events took place in the former building of
the stock exchange in Amsterdam, called:
“Beurs van Berlage”. Upon entering the
building for the first time we were given details on where our booth was and
where the talks would take place — setting up our booth and planning the shifts
was just another thing to do before exploring the Haxpo area:
a) if you’re interested in the technical details of these attacks (and
mitigation advice), pls see
this excellent technical
report the Broadband Internet Technical Advisory Group published last year
(apparently Comcast
had observed
such attacks before).
b) Daniel and I gave a
talk on attacking SNMP
at HITB Dubai 2007 (Hi Amy & Dhillon! 😉) laying
out the basic idea for that type of attack and we later described it in a bit
more detail at ShmooCon 2009 where we
even demoed it publicly (camera recording stopped at that point, for obvious
reasons). We used (a slightly modified version of)
this tool.
From the research we did at the time we can confirm this was/presumably still is
a huge problem, at least for European carriers’ broadband segments (acting as
amplifiers).
This is a short summary of some selected talks from the first day of this year’s
Hack in the Box
conference in Amsterdam.
Abusing Twitter’s API and OAuth Implementation by Nicolas Seriot
Nicolas Seriot (https://twitter.com/nst021) is an iOS Cocoa developer with an
interest in privacy and security. He is currently a mobile applications
developer and project manager in Switzerland. Nicolas focused his talk on the
extraction of consumer tokens that are needed for OAuth to authenticate a
consumer to a service provider. These tokens can then be used by rogue
applications to gain access to a victims twitter account.
This is a short summary of some selected talks from the second day of this
year’s Hack in the Box conference in Amsterdam.
Rethinking the Front Lines by Bob Lord
Bob Lord is currently the Director of Information Security at Twitter. He has
worked at numerous companies in the area of security and software engineering.
In his keynote for the second day of HITB13AMS he tackled a topic that has
raised a lot of discussions in the past months. His talk was a summary of what
twitter does internally to ensure the security of the company and a plea to
implement so called security awareness trainings for employees in a sustainable
way.
A
quick update on the workshop we’ve just finished at
Hack in the Box 2012 Amsterdam:
Due
to popular demand we decided to bring the slides online without wasting any more
time. The official website of the conference is currently experiencing some
problems due to high interest in all the stuff what was released in the last two
days. Great conference!
Hi,
didn’t find the time so far to post a short blog about
HITB Amsterdam so far…
but here we go.
Unfortunately I couldn’t arrive in AMS earlier than Thursday evening so I missed
the first day (and – from what I heard – some great talks). However we went out
for dinner that night with the likes of Andreas (Wiegenstein), Jim (Geovedi),
Raoul (Chiesa), Travis (Goodspeed), Claudio (Criscione) and some more guys and I
had some quite good conversations, both on technical matters and on
Intra-European cultural differences ;-). Btw: thanks again to Martijn for taking
care of the restaurant.
 A
quick update on the workshop we’ve just finished at