This is my short write up on Daycon X1, 2017. The
summit was held at Dayton, the land where
Wright brothers were born.
Apart from being my first US trip, I also gave my first training on Hacking 101
also called the Bootcamp.
The Daycon X1 bootcamp started on 18th September. Ahmad, my colleague focused
on web security, network scanning and metasploit exercises. I mainly handled
classes on reversing and binary exploitation along with some pcap anaylsis and
network attacks. It was highly fulfilling experience to give a workshop.
Teaching is definitely the best way to learn any topic by digging deep into
it.The simpler you can explain, the more clarity you have on the topic. But I
must say that it was indeed exhausting by the end of three days.
Just a few days ago I had the pleasure of visiting
Day-Con X. I listened to some great talks in the closed
and public sessions. Since the first day was the security summit (closed
session) I will just name a few titles with some brief words.
Captivating Security – Safety versus Passion (Josh More):
Was quite interesting to compare the IT-World with zoos.
Beyond Embedded (Brittany Postnikoff):
Robots are fun soon :).
As you might have read,
I recently had a closer look at how easy it actually is to become part of an IoT Botnet.
To start a further discussion and share some of my findings I gave a quick
overview at the recent Dayton Security Summit. The Mirai
Botnet was supposed to be one of the case studies here. But the way things go if
one starts diving into code…I eventually gave an overview of how the Mirai Bot
actually works and what it does. As such: Here a quick summary of the Mirai
Botnet bot.
As described in my previous post,
KrebsonSecurity.com was attacked by a major DDoS attack.
Reaching between 620Gbps and 660Gbps it was the largest documented DDoS attack
so far. The attack seemingly resulted from a Botnet called Mirai. Shortly after
the attack, a
post on hackforums
claimed to contain the actual source code of just this botnet.
The source code consists of
three projects: The bot itself with its CnC server and a loader component.
In mid-October our friend Bryan Fite aka Angus Blitter invited the community for
the ninth edition of Day-Con. Bryan’s annual security
summit, which we regard as the sister event of TROOPERS, is a pretty good reason
to visit lovely Dayton, Ohio.
And so we did… ERNW sent in five delegates. Delegates is Day-Con-speak for all
attendees and speakers and such a subtle choice of wording sets the tone for the
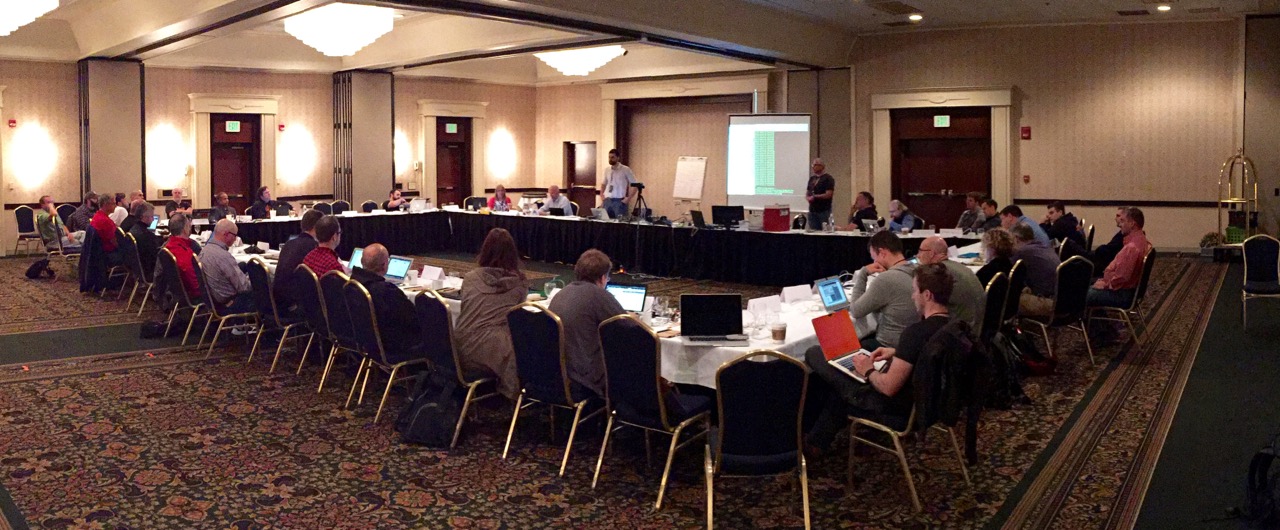
whole event. People seemed to be really focused and the
roundtable-like setting during the talks (see above) provided a cozy atmosphere
for in-depth expert chatting.
Some of us had the pleasure to participate in this year’s
Daycon VII, three days of Real Hacking and Relevant
Content, in Dayton, OH. The event began on September 16th with the Packetwars
bootcamp. We had the chance to teach some really promising young students and to
prepare them for the Packetwars battle that was scheduled four days later. The
students had to go through topics like Windows security, network security and
web application security both practical and in theory.
Two weeks ago we had a great time at
Day-Con VI. Enno, Matthias, Rene, Frank and
me traveled to Dayton, OH to give workshops and presentations. We started a
tough week full of workshops on Tuesday where
Rene gave a deep inside look into the world of security on current mobile
platforms. Matthias discussed security problems and possible design patterns of
cloud environments in his Cloud & Virtualization Security Workshop before he
gave a first insight into the world of reverse engineering on Wednesday. Frank
and me taught the basics of hacking and pentesting in the
PacketWars bootcamp (comparable to the one at
TROOPERS),
preparing the participants for the
PacketWars on Saturday. Obviously we were
not the only ones having a
great time
😉
As every year, we
will be attending Day-Con, a one-day security summit in
Dayton, OH — this year for its VIth edition. Even though the actual conference
comprises “only” one day full with talks and discussions (please find the agenda
here), the overall event
consists of trainings before the conference
and PacketWars battles (including an infamous party)
afterwards. Since we will be leading and attending some of the training
sessions, those might be of particular interest for people who missed our
Troopers workshops — so
you don’t have to wait a whole year but get another chance in October 😉
During the last days, some of our guys (including me) had some great days in
Dayton. Rene, Christopher, Hendrik, Sergej, and me flew in to give workshops and
presentations at Day-Con as well as to compete
in the infamous PacketWars game. While Day-Con is a
one day event, the two days before the conference comprised workshops on
secure iOS integration
(given by Rene) and
IPv6 security
(given by Christopher). Since the overall topic of the conference was trust,
Rene gave a
keynote
on broken trust which was based exemplary trust analysis, development of a trust
metric, and different trust factors. Those trust factors were also used in my
talk about evaluation methodologies for
cloud service providers
(regular followers will recognize some of the content of both talks from
differentposts 😉 ).
There were also talks from Sergey Bratus, Graeme Neilson and Angus Blitter.
While Sergey proposed a sound (not to say academic 😉 ) definition on the
classification of vulnerabilities and their connection to
turing complete input languages,
Angus gave an introduction to
PowerLine technologies and laid out,
that these technologies still suffer from naive assumptions about trusted
networks (he also refered to
this).
The day after the conference, the ERNW Allstars had to defend their championship
title in PacketWars. Since the first battle was scheduled for 10AM, we had quite
some time to tan in the sunny 30°C weather, recover from the conference and
prepare the expected victory celebration (some of you might remember some
“Champagne tradition” from Troopers). In face of this
motivation, we rushed through the 3 battles and were able to score first place
second year in a row. At this point, kudos to the two other participating teams
who gave us a tough battle, especially during the reversing challenges.
… which was, as in the years before, an awesome event.
Great talks, great people, great fun.
Bruce Potter gave a keynote
which did exactly what a good keynote should do: make the audience think and
entertain it at the same time.
[Those readers familiar with ERNW’s security model will certainly notice that
we do not necessarily agree with everything he said. We still think that – in
particular in times where infosec resources are scarce anyway – putting your
bets on prevention provides a better cost/[security] benefit ratio than going
for extensive detection capabilities.
Fix the doors first, then think about installing a CCTV.
Still, human nature tends to exchange “good security with low visibility” for
“poor security with potentially good visibility” quite easily… as can be noted
every day in many environments.]