This is my short write up on Daycon X1, 2017. The
summit was held at Dayton, the land where
Wright brothers were born.
Apart from being my first US trip, I also gave my first training on Hacking 101
also called the Bootcamp.
The Daycon X1 bootcamp started on 18th September. Ahmad, my colleague focused
on web security, network scanning and metasploit exercises. I mainly handled
classes on reversing and binary exploitation along with some pcap anaylsis and
network attacks. It was highly fulfilling experience to give a workshop.
Teaching is definitely the best way to learn any topic by digging deep into
it.The simpler you can explain, the more clarity you have on the topic. But I
must say that it was indeed exhausting by the end of three days.
In mid-October our friend Bryan Fite aka Angus Blitter invited the community for
the ninth edition of Day-Con. Bryan’s annual security
summit, which we regard as the sister event of TROOPERS, is a pretty good reason
to visit lovely Dayton, Ohio.
And so we did… ERNW sent in five delegates. Delegates is Day-Con-speak for all
attendees and speakers and such a subtle choice of wording sets the tone for the
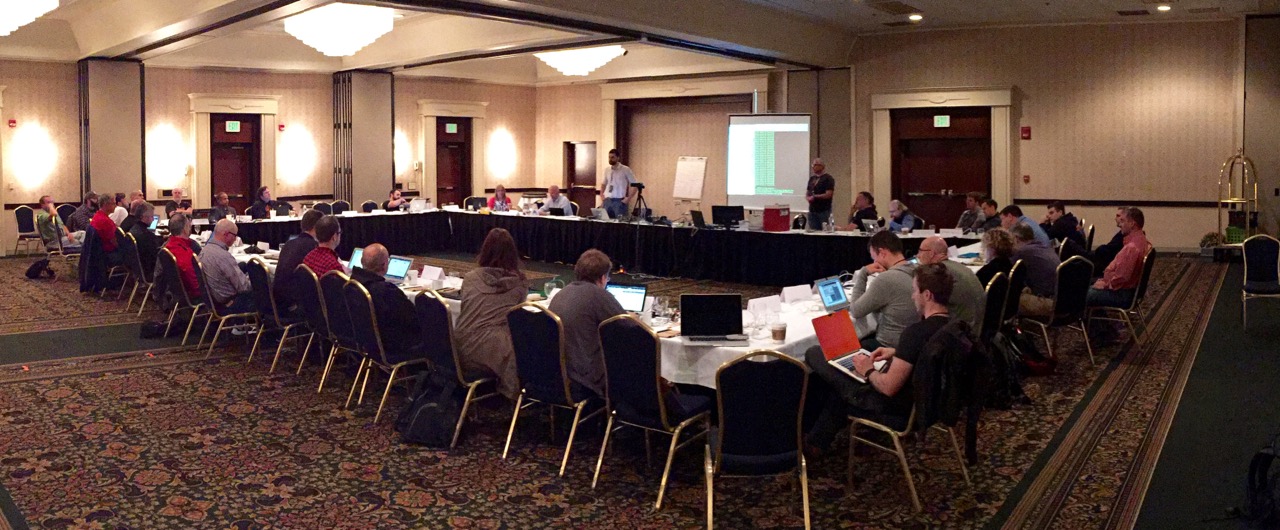
whole event. People seemed to be really focused and the
roundtable-like setting during the talks (see above) provided a cozy atmosphere
for in-depth expert chatting.
This year’s PacketWars contest at Troopers was a
blast! Under the topic of “Connected Car” the teams faced several different
challenges, which we will describe (as a debriefing) here.
You and your krew are “freelancers” hired to identify and neutralize an unknown
threat agent who has created weaponized software and delivered it to civilian
Connected Cars via compromised EV (Electrical Vehicle) charing stations. To make
matters worse there are indications that new strains of the malware are
appearing as the “worm” spreads from car to car. The mobile mesh network created
by the Connect Car is highly resilient, allowing the malware to spread
exponentially. Time is of the essence.
Malware analysis suggests that besides a botnet module, there is an active
CANBus injection capability. There appears to be other modules but they haven’t
been properly reversed and analyzed yet.
We’re currently starting the preparation for the
Troopers15PacketWars Challenge, and since I’ve participated in
quite some CTF games and have been involved in the preparation of a number of
PacketWars Battles, I thought I’d write down some thoughts on the design of
hacking challenges.
First of all, my experience is limited almost exclusively to attack-defend-CTFs
or interactive war games (such as PacketWars or
CCDC).
While thinking about this blogpost, I also came across several terms which are
used, so I decided to give a short summary:
During the last days, some of our guys (including me) had some great days in
Dayton. Rene, Christopher, Hendrik, Sergej, and me flew in to give workshops and
presentations at Day-Con as well as to compete
in the infamous PacketWars game. While Day-Con is a
one day event, the two days before the conference comprised workshops on
secure iOS integration
(given by Rene) and
IPv6 security
(given by Christopher). Since the overall topic of the conference was trust,
Rene gave a
keynote
on broken trust which was based exemplary trust analysis, development of a trust
metric, and different trust factors. Those trust factors were also used in my
talk about evaluation methodologies for
cloud service providers
(regular followers will recognize some of the content of both talks from
differentposts 😉 ).
There were also talks from Sergey Bratus, Graeme Neilson and Angus Blitter.
While Sergey proposed a sound (not to say academic 😉 ) definition on the
classification of vulnerabilities and their connection to
turing complete input languages,
Angus gave an introduction to
PowerLine technologies and laid out,
that these technologies still suffer from naive assumptions about trusted
networks (he also refered to
this).
The day after the conference, the ERNW Allstars had to defend their championship
title in PacketWars. Since the first battle was scheduled for 10AM, we had quite
some time to tan in the sunny 30°C weather, recover from the conference and
prepare the expected victory celebration (some of you might remember some
“Champagne tradition” from Troopers). In face of this
motivation, we rushed through the 3 battles and were able to score first place
second year in a row. At this point, kudos to the two other participating teams
who gave us a tough battle, especially during the reversing challenges.