“Nein! Ein von unbeugsamen Galliern bevölkertes Dorf hört nicht auf, dem
Eindringling Widerstand zu leisten.”
This is a famous quote pretty much every German kid used to know. Not sure if
this still applies though, my three haven’t touched Asterix comics so far.
Anyhow, you might ask why I cite this.
Simple answer: see
this recent article
from the Guardian on a Utah-based ISP “resisting some pressure”. That’s the
spirit…
When teaching courses on topics like Reverse Engineering or Malware Analysis we
always emphasize the need to minimize unneeded work. Because reversing an
unknown binary is a time consuming and complex process, tools that simplify the
RE process are invaluable when working under time pressure. In this blogpost
series I will present multiple tools and techniques that can help to reverse an
unknown binary. Please note that these articles do not contain cutting edge
research but rather target at newcomers. However, I hope to also provide some
useful and interesting information for moreexperienced practitioners.
Microsoft released
EMET v4.0 with
a new (security) feature that enables protection against fraudulent websites or
compromised root certification authorities (do you remember Comodo, DigiNotar,
DigiCert, Turktrust et al. ;-)?)
EMET defines via “certificate trust“ a trust chain between the domain name of a
website (and its associated website certificate) and a root CA certificate. This
is done through so called “pinning rules”. Here is one of the default pinning
rules of EMET 4.0 for the domain name login.live.com:
**Dear blog followers, TROOPERS speakers & attendees,
**we hope you’re doing fine! Today we have a couple of great things to share
with you:
TROOPERS14
Let’s start with a date. Get your calendar and mark March 17th – 21st 2014.
It’s your TROOPERS14 holidays. One week full of high-end education, workshops,
talks, reconnecting with friends, action, delicious food and one or the other
party. You know the drill – more details further down.
After his great presentations on
IPv6 Extensions Headers
and
security problems related to fragmentation
we had invited Antonios Atlasis to Heidelberg to give
this workshop
at ERNW. It was a great experience with many fruitful discussions between the
participants (mostly security practitioners from very large organizations
planning to have their Internet edge IPv6 enabled within the next 6-12 months)
and him/us. Antonios thankfully decided to make his
slides
and
scripts
available for those interested in further research on the topics (it should be
noted that the scripts have not been tested thoroughly and he’s happy to receive
feedback of any kind at antoniosDOTatlasisDOTgmailDOTcom). Today Marc (Heuse)
gives
his workshop
on pentesting in the IPv6 age. Hopefully such events help to move things into
the right direction in the IPv6 security space…
From
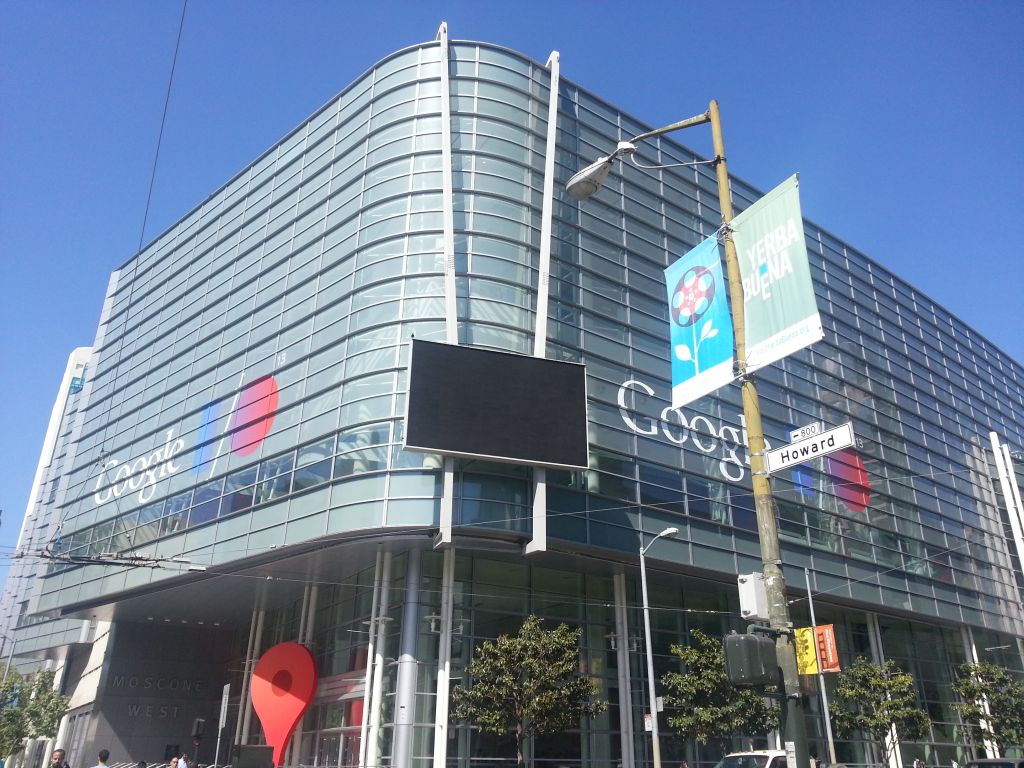
15th – 17th of May, the sixth Google I/O conference took place in San Francisco,
California and I was one of the lucky guys attending. More then 5500 people,
primarily web, mobile, and enterprise developers, attended this annual event. A
lot of presentations included announcements of new and exciting technologies,
APIs as well as of two new devices.
During the first minutes of the
keynote
some of Google’s managers announced that by now over 900 million Android devices
are activated and that 48 billion apps are installed, which demonstrates that
this market is still heavily growing. As the major part of the audience were
(app-) developers, these numbers were received quite greatfully and euphoric.
In the course of a current virtualization research project, I was reviewing a
lot of documentation on hypervisor security. While “hypervisor security” is a
very wide field, hypervisor breakouts are usually one of the most (intensely)
discussed topics. I don’t want to go down the road of rating the risk of
hypervisor breakouts and giving appropriate recommendations (even though we do
this on a regular base which, surprisingly often, leads to almost religious
debates. I know I say this way too often:I’ll cover this topic in a future post
;)), but share a few observations of analyzing well-known examples of
vulnerabilities that led to guest-to-host-escape scenarios. The following table
provides an overview of the vulnerabilities in question: