There are lots of interesting places to visit in Amsterdam, but if you are there
between the 26th and the 29th of May, then our booth at HAXPO exhibition should
be your main destination.
HAXPO is a great exhibition, where you can
become up-to-date with the latest security technologies, attend various
workshops and get in touch with more than 35 IT and information security
companies. It will take place in the beautiful historical building “Beurs van
Berlage” in the center of Amsterdam. As usual, ERNW will take part in HAXPO. We
will be waiting for you in the Community Village section (booth NL-018). Come
visit and get to know more about us. You are invited to take our hacking
challenges, where the levels of complexity vary from beginners to advanced.
Furthermore, we will bring our KNX hacking suitcase!
In our
talks
in the past we showed what might be possible if an attacker gets access to
backhaul and/or core network of a telecommunication provider. In a security
analysts perspective this is really disgusting, but provider always will
argument that those attack scenarios are not realistic.
Because of legal restrictions we are not able to demonstrate this in practice
(e.g. by breaking in into a BTS environment somewhere in the woods) but what we
can do is this: building a lab.
Sometimes it is really shocking what you can buy on Ebay, right? Here we got one
very interesting component: a Huawei BBU3900 BaseStation which is used by a
couple of providers. Okay, it is for GSM-Rail, but the technology behind is very
equal. And for 100 dollars (plus shipping) you don’t ask further questions…
A few days later than planned (sorry about that), but here we go with part 2
(Part1) and
the demodulation/analysis part.
Initial Analysis
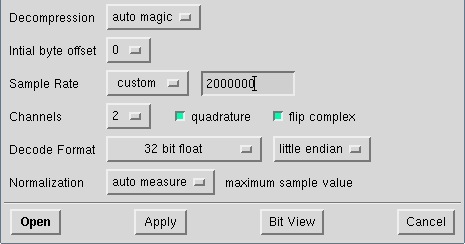
To analyse a captured signal, the tool baudline seems to be the best way at the
moment. So we open it with the following options and have a closer look
(ContextMenu->Input->Open file):
After using the open button, you should be able to see something similar to
this:
I attended this really nice conference in Slovenia on April
16th. It was a smaller conference, but very memorable for the people (students,
IT sec professionals and managers alike) who attended.
I also had the pleasure to present
on How secure am I with EMET?
and
Evaluating the APT armor and
wanted to share the slides with you — feel free to approach me for any kind of
feedback or discussion.
A while a go Dominik and I gave an introductory presentation about SSL at the
BASTA.NET conference, a developer-oriented event held in Darmstadt twice a year.
At that time there were quite some enthusiastic participants but recently we’ve
also gotten some inquiries asking for the relevant materials. Although there’s
no recording of the session, we’ve decided to put the slides here for those
interested who didn’t make it to the talk.
This year’s PacketWars contest at Troopers was a
blast! Under the topic of “Connected Car” the teams faced several different
challenges, which we will describe (as a debriefing) here.
You and your krew are “freelancers” hired to identify and neutralize an unknown
threat agent who has created weaponized software and delivered it to civilian
Connected Cars via compromised EV (Electrical Vehicle) charing stations. To make
matters worse there are indications that new strains of the malware are
appearing as the “worm” spreads from car to car. The mobile mesh network created
by the Connect Car is highly resilient, allowing the malware to spread
exponentially. Time is of the essence.
Malware analysis suggests that besides a botnet module, there is an active
CANBus injection capability. There appears to be other modules but they haven’t
been properly reversed and analyzed yet.
Introduction
This and the following two posts should serve as a step-by-step guide through
the whole process of analyzing a radio frequency black box, demodulate and
understand the data transfered and finally modulate our own data in order to
e.g. perform a brute force attacks.
The information provided and the results are immensely inspired by Michael
Ossmann and the workshops he has given at our location. Visit him and his great
tool HackRF at https://greatscottgadgets.com/hackrf/ !
This post is a short wrap-up of our Troopers talk about the research we did on
IBM’s General Parallel File System. If you are interested in all the technical
details take a look at our
slides
or the video recording. We will
also give an updated version of this talk at the
PHDays conference in Moscow next month.
The IBM General Parallel File System is a distributed file system used in large
scale enterprise environments, high performance clusters as well as some of the
worlds largest super computers. It is considered by many in the industry to be
the most feature rich and production hardened distributed file system currently
available. GPFS has a long and really interesting history, going back to the
Tiger Shark file system created by IBM 1993.