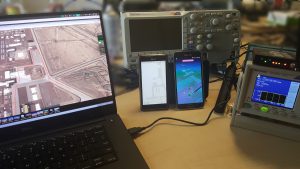
The moment, when your team leader asks you to cheat at Pokémon GO…everyone knows
it, right? No? Well, I do 😉
GPS Spoofing Setup
As I’m not a gamer, the technical part was of much more interest – that’s the
real gaming for me.
So, challenge accepted!
In the past I was often fiddling around with SDR (Software Defined Radio),
started with DVB-T sticks some years ago. When I came to ERNW in 2014 I got in
touch with
Michael Ossman’s great HackRF One for
the first time, and subsequently my thesis was based on SDR.
Today we received a few
ShareBrained Technology – PortaPack H1
to use with our HackRFs. Having done a first few minutes of scanning, I just
wanted to give you a quick overview of its features and potential…
After having had
Michael Ossmann in
for a few workshops with his
Jawbreaker and
HackRF One
we have used the HackRF on multiple occasions. No matter if
research projects
or actual customer projects, the HackRF has always been of great help. As we
mainly use it on laptops, we’ve got certain constraints concerning its
portability when wanting to do some quick mobile scanning. Although there are a
few solutions for tablets and smartphones, they haven’t been quite able to
convince all of us. So a while back we decided to keep an eye on the
PortaPack and
have been since been waiting for its release.
A few days later than planned (sorry about that), but here we go with part 2
(Part1) and
the demodulation/analysis part.
Initial Analysis
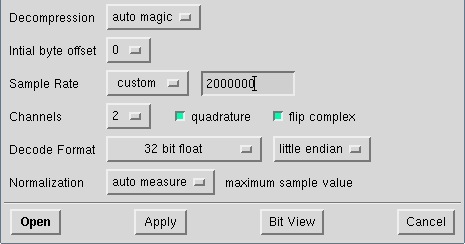
To analyse a captured signal, the tool baudline seems to be the best way at the
moment. So we open it with the following options and have a closer look
(ContextMenu->Input->Open file):
After using the open button, you should be able to see something similar to
this:
Introduction
This and the following two posts should serve as a step-by-step guide through
the whole process of analyzing a radio frequency black box, demodulate and
understand the data transfered and finally modulate our own data in order to
e.g. perform a brute force attacks.
The information provided and the results are immensely inspired by Michael
Ossmann and the workshops he has given at our location. Visit him and his great
tool HackRF at https://greatscottgadgets.com/hackrf/ !
once again, we welcomed Michael Ossmann at the ERNW headquarters for fun with
SDR. This time with Mike´s advanced SDR workshop. And to be up front about it…it
was plain awesome. For everybody who is not familiar with Software Defined Radio
(SDR): Let’s regard it as the ultimate tool when working with radio signals.
Take a look a
this to learn
more.
Mike showed us the new revision of his HackRF One and explained us some more
advanced techniques when it comes to Radio Frequnecies hacking. Compared to last
time, the workshop focused on reversing signals and how to synthesize them. So
this time we were crafting RF packets ourselves instead of just replaying a
capture. This introduces different attack types which can be carried out over
the air for example bruteforcing or fuzzing of radio devices.
today we welcomed Michael Ossmann at the
ERNW headquarter for an exclusive workshop on his
HackRF
gadget. Everybody was quite excited to get hands-on with this shiny piece of
hardware, which is currently
crowd-funded on Kickstarter.
For everybody who’s not familiar
with Software Defined Radio (SDR):
Let’s regard it as the ultimate tool when working with radio signals.
Michael Ossmann in the house.
Let’s quote Michael’s campaign website:
Transmit or receive any radio signal from 30 MHz to 6000 MHz on USB power
with HackRF. HackRF is an open source hardware project to build a Software
Defined Radio (SDR) peripheral.