Truncating TLS Connections to Violate Beliefs in Web Applications Ben Smyth and Alfredo Pironti, INRIA Paris-Rocquencourt
This presentation was also given at
BlackHat
some weeks ago. It outlines a very interesting class of attacks against web
applications abusing the TLS specification which states that “failure to
properly close a connection no longer requires that a session not be resumed
[…] to conform with widespread implementation practice”. This characteristic
enables new attack vectors on shared systems where certain outgoing (TLS
encrypted) packets can be dropped in order to prevent applications from e.g.
correctly finishing transaction (such as log out procedures) or even modifying
the request bodies by dropping the last parts.
I have the pleasure to visit this year’s
USENIX Security Symposium
in Washington, DC. Besides the nice venue close to the
national mall, there are also
several co-located workshops. Every night I will try and provide a summary of
those presentations I regard as most interesting. However, I hope to manage to
keep up with it as there are a lot of interesting events, people to meet, and
still some projects to keep up with. The short summaries below are from the 6th
USENIX Workshop on Large-Scale Exploits and Emergent Threats.
That meeting was actually a
great event. Once more, big thanks! to Fernando for organizing it and to
EANTC for providing the logistics.
A couple of unordered notes to follow:
a) The slides of our contribution can be found
here.
Again, pls note that this is work in progress and we’re happy to receive any
kind of feedback.
[given Fernando explicitly mentioned Troopers, we’ve allowed ourselves to put
some reference to it into this version of the slide deck…]
Next to IETF 87 going on in Berlin
in a few days there will be an
informal meeting of the “IPv6 Hackers”
on Tuesday. We really look forward to personally meet a number of people who we
(so far) only know from the associated
mailing list or
similar machine-enhanced exchange. We hope to contribute as well. Based on the
stuff of
this workshop from
the
IPv6 Security Summit
at Troopers13 we might give a short project
presentation along the lines of “Some Notes on Testing the Real-World IPv6
Capabilities of Commercial Security Products”, providing an overview of some
testing done on commercial gear, together with a discussion of testing
approaches, tools and key aspects.
**Dear blog followers, TROOPERS speakers & attendees,
**we hope you’re doing fine! Today we have a couple of great things to share
with you:
TROOPERS14
Let’s start with a date. Get your calendar and mark March 17th – 21st 2014.
It’s your TROOPERS14 holidays. One week full of high-end education, workshops,
talks, reconnecting with friends, action, delicious food and one or the other
party. You know the drill – more details further down.
From
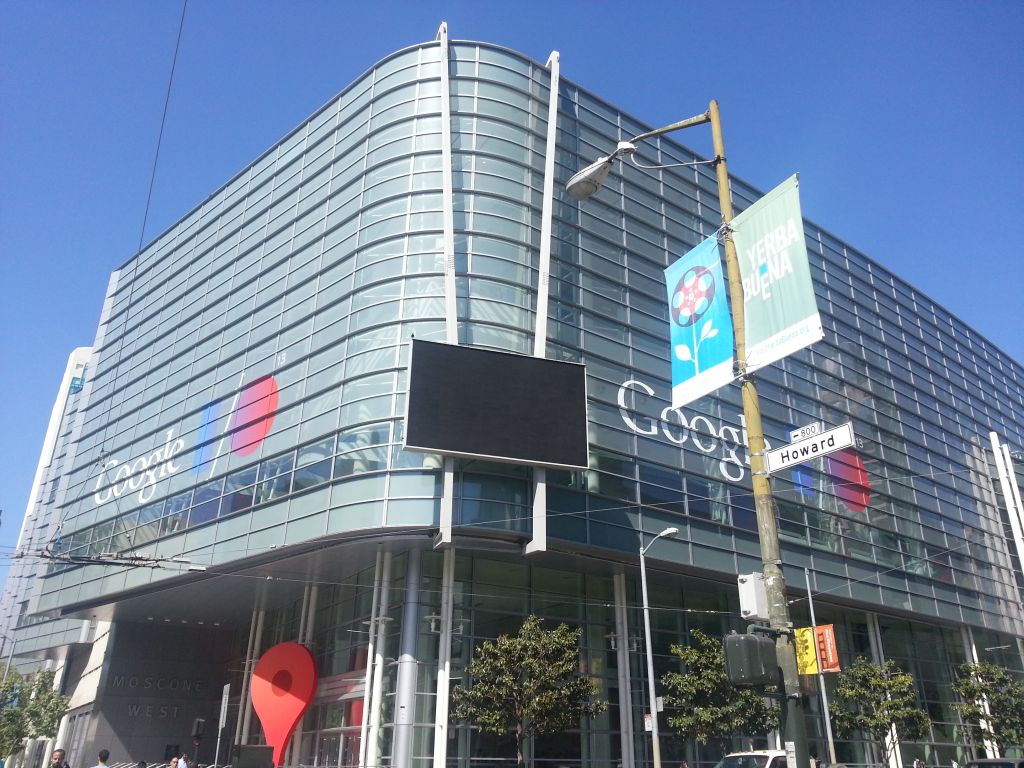
15th – 17th of May, the sixth Google I/O conference took place in San Francisco,
California and I was one of the lucky guys attending. More then 5500 people,
primarily web, mobile, and enterprise developers, attended this annual event. A
lot of presentations included announcements of new and exciting technologies,
APIs as well as of two new devices.
During the first minutes of the
keynote
some of Google’s managers announced that by now over 900 million Android devices
are activated and that 48 billion apps are installed, which demonstrates that
this market is still heavily growing. As the major part of the audience were
(app-) developers, these numbers were received quite greatfully and euphoric.
just to let you know that all presentations from this year’s
TelcoSecDay
are published in the interim. (Harald [Welte] couldn’t participate as in the
morning of that day FRA airport was closed on short notice).
This is a short summary of some selected talks from the first day of this year’s
Hack in the Box
conference in Amsterdam.
Abusing Twitter’s API and OAuth Implementation by Nicolas Seriot
Nicolas Seriot (https://twitter.com/nst021) is an iOS Cocoa developer with an
interest in privacy and security. He is currently a mobile applications
developer and project manager in Switzerland. Nicolas focused his talk on the
extraction of consumer tokens that are needed for OAuth to authenticate a
consumer to a service provider. These tokens can then be used by rogue
applications to gain access to a victims twitter account.