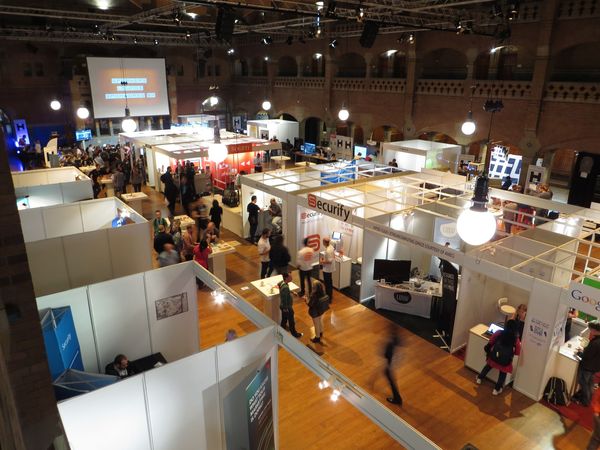
This week I had the pleasure to attend BruCON 2014.
While participating at the Brucon 5×5 program, I had also the chance to attend
this well-known European Con which is held in the beautiful city of Ghent.
The main event took place two days (on 25th and 26th of September), while some
very interesting trainings were given in the previous days. There was mainly one
track, plus some workshops that you could also attend, if you wished. You could
book your seat at one of the workshops using an
on-line scheduling system.
Information security conferences are known to be attended because of several
reasons. For some it’s the technical content, for others the networking
potential and for some others simply meeting old friends. Pinpointing our
motives is clearly a challenging task, but the following wrap-up ought to share
our personal highlights of the week we spent visiting Black Hat USA 2014 and
DEFCON 22 in Las Vegas.
After somewhat 18 hours of flight, some sleep and with the beautiful scenery of
perpetual clear skies above Las Vegas we began what was to be an incredible
week.
Last week we had the opportunity and pleasure to present some of our research
results at BlackHat US 2014 (besides of meeting a lot of old friends and having
a great researchers’ dinner).
Enno and Antonios gave their presentation on IDPS evasion by IPv6 Extension
Headers, described
here.
The material can be found
here: Slides,
tools (the main tool used was Chiron,
authored by Antonios) &
whitepaper.
Ayhan and me presented our results of the security analysis of Cisco’s
EnergyWise protocol. The protocol enables network-wide power monitoring and
control (ie turning servers off or on, putting phones to standby — basically
controlling the power state of all EnergyWise-enabled or PoE devices). The main
problem (besides a DoS vulnerability we found in IOS, see
official Cisco advisory)
is its PSK-based authentication model, which enables an attacker to cause
large-scale blackouts in data centers if the deployment is lacking certain
controls (for example our good old favorite, segmentation…). There will be a
longer blogpost/newsletter on this topic soon.
The material can be found
here: Slides &
tools
Past month we (which is me and a group of other ERNW students, supported by some
of the “old” guys — I hope my team lead won’t yell at me for this 😉 ) attended
the Haxpo and Hack in the Box in Amsterdam. Starting from 28. May, we had three
days at this great conference (HITB) and exposition
(Haxpo). The two events took place in the former building of
the stock exchange in Amsterdam, called:
“Beurs van Berlage”. Upon entering the
building for the first time we were given details on where our booth was and
where the talks would take place — setting up our booth and planning the shifts
was just another thing to do before exploring the Haxpo area:
and thanks for a great time at HES14! A nice
venue (a museum), sweet talks and
stacks of spirit carried us through the three day con. It all set off with a
keynote byTROOPERs veteran Edmond ‘bigezy’ Rogers, who stuck to a quite simple
principle: “People do stupid things” and I guess every single one of you has
quite a few examples for that on offer. Next to every speaker referenced that
statement at some point during her/his talk. Furthermore we presented an updated
version of our talk
LTE vs. Darwin,
covering our research of security in LTE networks and potential upcoming
problems.
This is a guest post from Vladimir Wolstencroft from our friends of
aura information security
==================================================================
Mobile messaging applications have been occupying people’s attention and
it seems to be all the latest news. Perhaps I should have called my presentation
the 19 Billion dollar app but at the time of writing and research I thought the
proposed 3 Billion dollar amount for SnapChat was a little ludicrous, who could
have known that would have been just a drop in the ocean.
Given we’ve received a number of inquiries as for the agenda of this year’s
TelcoSecDay here’s a first preliminary agenda. To get an idea of the event’s
character you might have a look at the agenda of the
2012 edition
or the
2013 edition.
Pls note that there might be changes/additions to the following outline as we’re
currently discussing potential contributions with two European operators. Here
we go, for today:
9:00: Opening Remarks & Introduction
9:15: Ravi Borgaonkor – Evolution of SIM Card Security
10:15: Break
10:45: Adrian Dabrowski
11:45: Collin Mulliner – PatchDroid – Third Party Security Patches for Android
12:30: Lunch
13:45: Philippe Langlois
14:45: Break
15:15: Haya Shulman – The Illusion of Challenge-Response Authentication
16:00: Christian Sielaff & Daniel Hauenstein – Breaking Network Monitoring Tools
Used in Telco Space
16:30: Closing Remarks
19:00: Joint dinner (hosted by ERNW) in Heidelberg Altstadt for those interested
and/or staying for the main conference
Hey guys,
as some of you may have noticed, just recently at ShmooCon we gave our talk “LTE
vs. Darwin” (Slides
here).
There we presented some results of our research in 4G telco network security.
Some of those originate from our research contribution to
ASMONIA, but we expanded the scope and also took a look at the
air interface. Both the air interface and the backend links & protocols must be
secured appropriately; otherwise communication may be eavesdropped or sensitive
information may be compromised. In the following we want to provide an overview
of LTE main components and potential attack vectors.
Last weekend, from 17 to 19 January, ShmooCon was
held in Washington, DC. A number of different topics was covered in great talks
and we want to give you a short overview of the conference. In the following our
favorite talks are briefly summarized.
Privacy Online: What Now?
Ian Goldberg, one of the designers of the
OTR Protocol, gave the
keynote on the first day. His talk was quite interesting and he presented some
really nice approaches, one of those being an attack against PGP. He described
the attack as follows: an attacker could copy a key server by downloading all
the stored keys. If this is done it is possible to create new key pairs with
exactly the same settings as the keys downloaded. The third step is to create
all the signing links between the keys as they exist on the real key server.
Finally, the attacker uploads these new keys including the signing links to the
original key server.
Now, in case Alice wants to retrieve the public key of Bob, Alice would find two
keys with seemingly identical properties. If choosing the wrong key for
encryption the message will be decipherable by the attacker and in case of MitM
situation be accessed. Furthermore, if Alice then signs the “mirror key”, the
cloned keys and the original would merge, resulting in further problems.
This was just one consideration discussed in Goldberg’s talk. For the full
content, watch the recording, available soon on ShmooCon page.
Today we have to pleasure to announce another round of
Troopers talks.
Here we go:
Noam Liram: Vulnerability Classification in the SaaS Era FIRST TIME
MATERIAL
Abstract: In this talk we will thoroughly analyze two major SaaS vulnerabilities
that were found by Adallom (one of which is still in responsible disclosure
stages at the time of writing). By demonstrating this new class of exploits
which we have nick-named “Ice Dagger” attacks, we aim to change the current
industry-wide criteria for vulnerability classifications, which were developed
in the Desktop/Server world, are inadequate when classifying SaaS
vulnerabilities. We will specifically discuss the details of MS13-104.