Here at TROOPERS HQ we are well into the Holiday (read TROOPERS) Spirit so we
thought we would publish another round of talks! The current agenda can be
found here.
Happy Holidays!
Your TROOPERS Team
===
2nd Day Keynote FIRST TIME TROOPERS SPEAKER
Bio: Ben Zevenbergen joined the Oxford Internet Institute to pursue a DPhil
on the intersection of privacy law, technology, social science, and the
Internet. He runs a side project that aims to establish ethics guidelines for
Internet research, as well as working in multidisciplinary teams such as the EU
funded Network of Excellence in Internet Science. He has worked on legal,
political and policy aspects of the information society for several years. Most
recently he was a policy advisor to an MEP in the European Parliament, working
on Europe’s Digital Agenda. Previously Ben worked as an ICT/IP lawyer and policy
consultant in the Netherlands. Bendert holds a degree in law, specialising in
Information Law.
Here’s the second round of TROOPERS16 talks. For more information check out our
website: TROOPERS
Happy Holidays and all the best for 2016 to everybody!
Your TROOPERS Team
===
Ivan Pepelnjak: Real-life Software-Defined Security
Vendors, pundits, and industry media love to talk about Software-Defined
Everything, but nothing ever changes in the enterprise world, right? Wrong. Some
engineers are already solving security problems with a software-defined approach
to networking and security, be it microsegmentation in NSX or OpenStack
environment, building scale-out IDS clusters, or respond to DoS or intrusion
events in real-time… and we’ll cover all these ideas in this fast-paced
presentation
Here’s the first round of TROOPERS16 talks. For more information check out our
website: TROOPERS
Happy Holidays and all the best for 2016 to everybody!
Your TROOPERS Team
===
Mike Ossmann: Rapid Radio Reversing
Wireless security researchers have an unprecedented array of tools at their
disposal today. Although Software Defined Radio (SDR) is the single most
valuable tool for reverse engineering wireless signals, it is sometimes faster
and easier to use other tools for portions of the reverse engineering process.
I’ll discuss how beneficial a hybrid SDR/non-SDR approach has been to security
researchers, and I’ll walk through an example of the process.
“Welcome to Brazil”, I think, turned to being the most used statement during the
past Hackers to Hackers Conference in Sao Paulo. It was used as the main
reaction to every speech taking moment, and there were a lot of those! To honor
the moments and give you a quick insight into was what going on in Sao Paulo,
here is a quick summary of the overall event and our own contribution.
we (Christopher, Jan-Pascal and me) had the pleasure to join the 7th
DENOG (German Network Operators
Group) meeting in Darmstadt
which takes place yearly in autumn. For the first time the meeting was scheduled
for two days which offered more time for talks and discussions than the previous
meetings. The concept of DENOG is to meet, talk, discuss and share experience
with the network operator community in Germany.
The meeting started withe a talk from Peter Sievers from Juniper about Network
Automation and Programmability. He presented why automation and programmability
is getting more and more important even for network operators. It will help to
automate the build process, the configuration and should ideally help you
operating and troubleshooting your envirnoment. The focus of the talk was on the
platforms which are already available and ready to use to automate day to day
activities.
Last week I had the pleasure to attend the “escar” (Embedded Security in
Cars) conference in Cologne, Germany.
Arriving late Tuesday, I had the chance to get a rich breakfast before joining
the con in the hotel Dorint at Cologne’s famous place the Heumarkt.
Unfortunately I had to deal with two stumbling blocks on my way to the Dobrint:
The magnetic sensor of my mobile which went crazy (no compass) and – the date.
11th of November in Cologne means just one thing – carneval! The whole
city was just in a state of exception. Everybody on my way to the venue seemed
to be drinking or beeing already drunk – at 9am! 😉
Being a little late, I went straight to the room after registration. As there
was only one track to follow you could not miss any talk – nice thing!
After we were welcomed by the hosts, and the first talk started.
Last week, on the 27th-28th I attended a nice wireless conference in berlin, the
WLPC (Wireless LAN Pros Conference). You can visit their website at
http://berlin2015.wlanprosconference.com.
This conference is a community-driven conference from wireless professionals
with focus on typical topics that come up when you are planning or running large
wireless networks. This is a mainly Twitter based community, you can see some
Tweets with hashtags #WLPC for example. There were also some interesting talks
about future networks, for example Marko Tisler gave a talk about wireless LAN
and SDN and what we can expect and what SDN will not solve for wireless
networks.
In mid-October our friend Bryan Fite aka Angus Blitter invited the community for
the ninth edition of Day-Con. Bryan’s annual security
summit, which we regard as the sister event of TROOPERS, is a pretty good reason
to visit lovely Dayton, Ohio.
And so we did… ERNW sent in five delegates. Delegates is Day-Con-speak for all
attendees and speakers and such a subtle choice of wording sets the tone for the
whole event. People seemed to be really focused and the
roundtable-like setting during the talks (see above) provided a cozy atmosphere
for in-depth expert chatting.
That was the opener for my presentation on the Security in Medical Devices at
CodeBlue 2015 last week in Tokyo, Japan. A
Code Blue
often describes a patient in a critical condition, mostly needing resuscitation.
That just seemed to be a perfect match, also in the sense that the condition of
some medical devices out there are still pretty critical concerning security. If
you follow our current research on this you know what I am talking about. I hope
that we are not talking about this topic anymore three years from now. That
would mean that we have made the world a safer place, although it took some time
… 😉
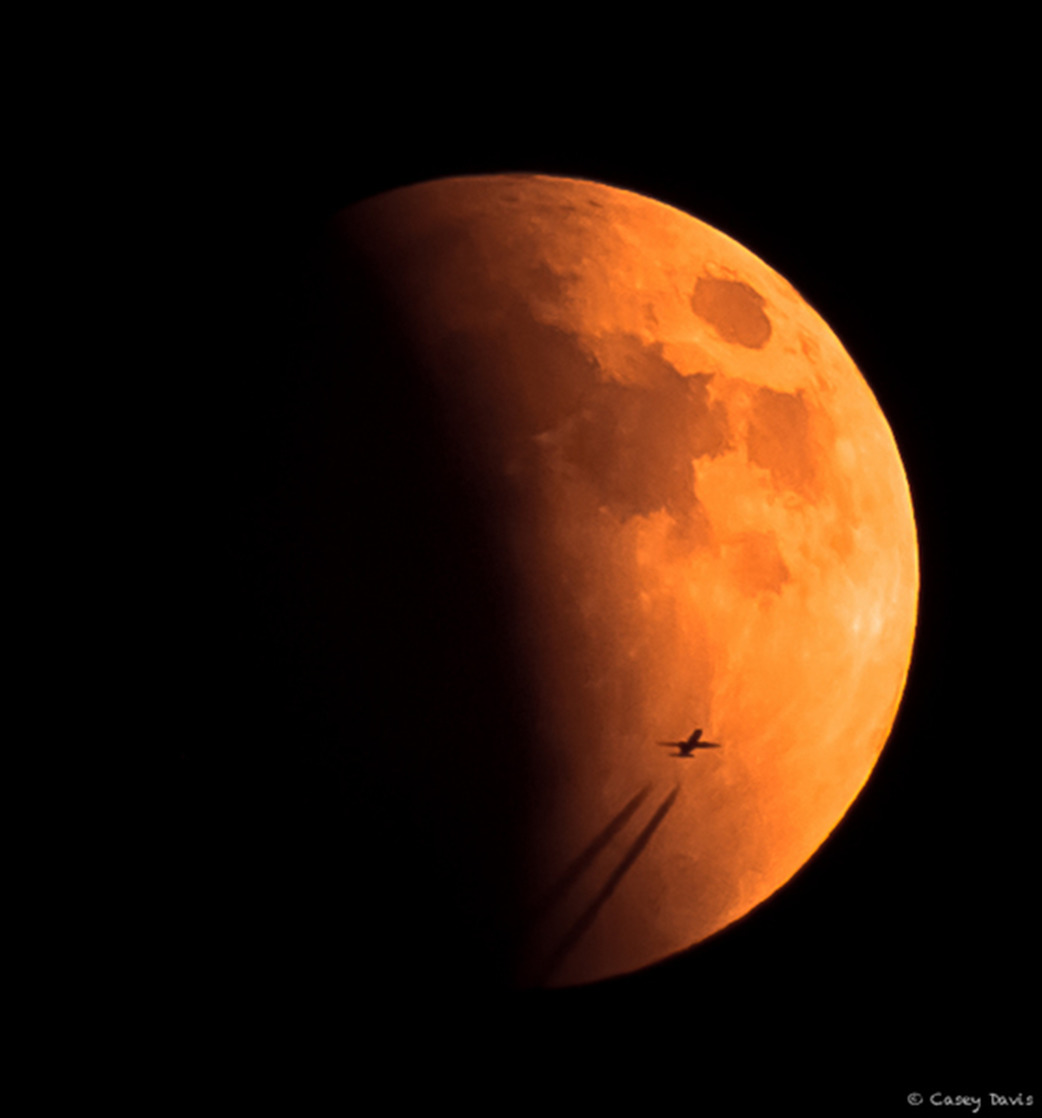
On Monday the 28th of September 2015 a rather rare event occurred. At around 4
a.m. the moon changed its colour into a dim of red, luckily the sky was clear
enough to see something.
If you missed that event your next chance will be in about 15 years or so.
The reason for being awake this early wasn’t the moon in the first place but
what followed afterwards – my trip to the
hardwear.io Security Conference in The Hague.