On Monday the 28th of September 2015 a rather rare event occurred. At around 4
a.m. the moon changed its colour into a dim of red, luckily the sky was clear
enough to see something.
If you missed that event your next chance will be in about 15 years or so.
The reason for being awake this early wasn’t the moon in the first place but
what followed afterwards – my trip to the
hardwear.io Security Conference in The Hague.
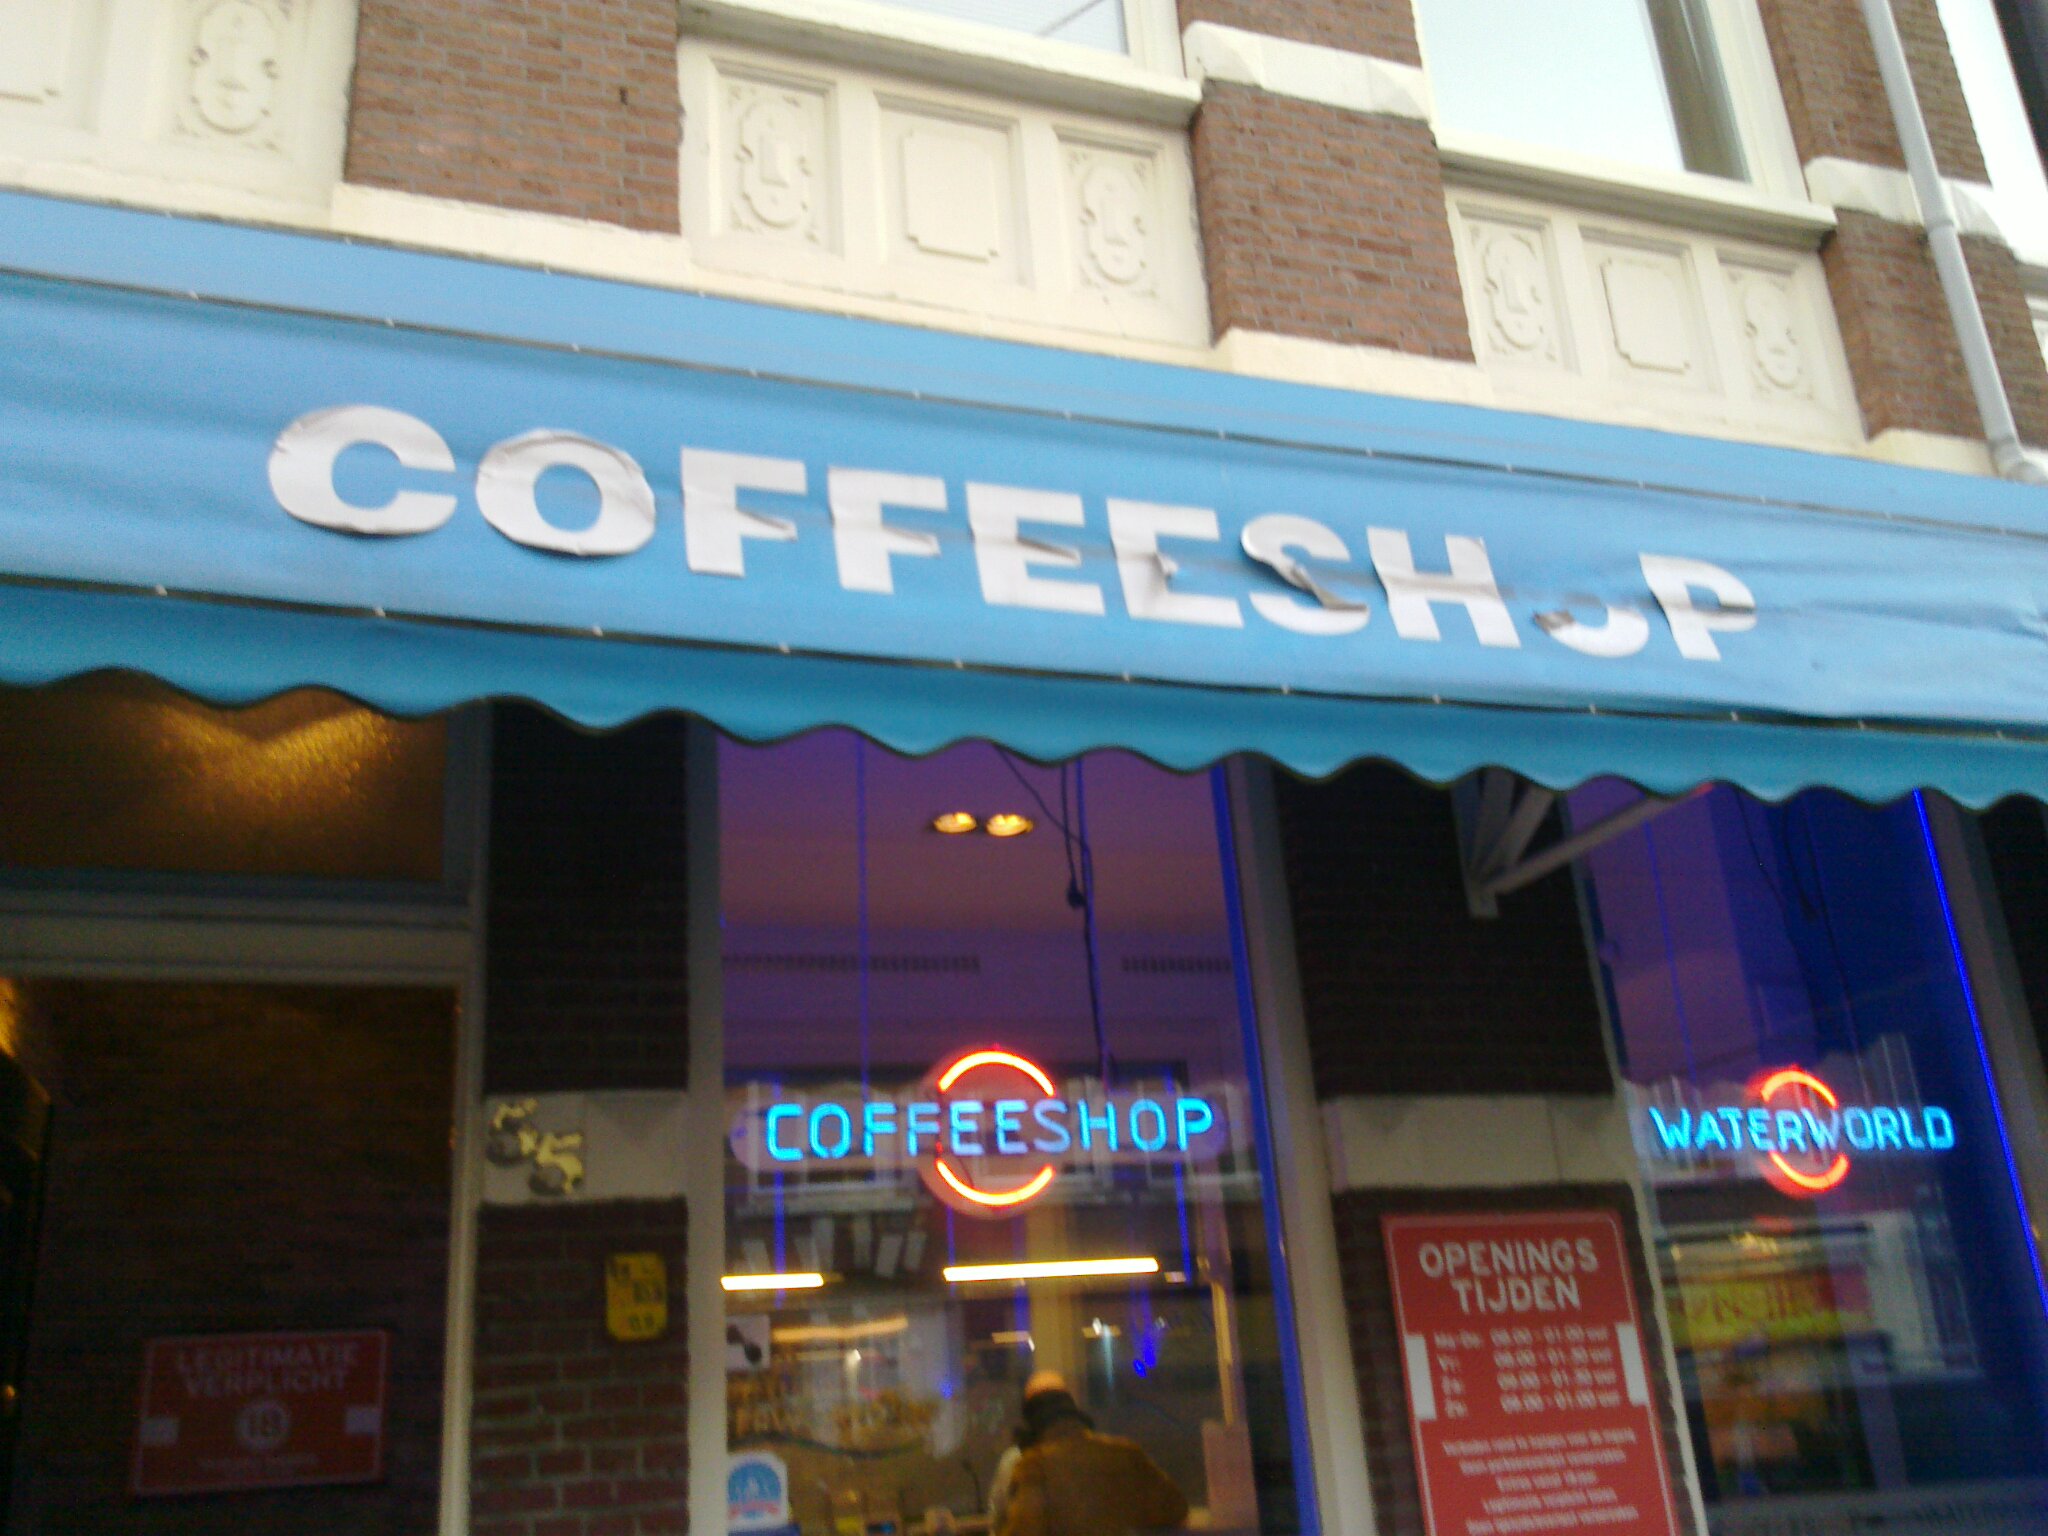
During my stay in The Hague I needed to print something, so I asked for a Copy
shop and this is where they sent me:
Against the common rule to just talk about the personal favorites, I will cover
all talks in one, two or more sentences (arbitrarily decided while
writing). This also gives you a broader picture of the conference.
Jumping right in with the keynote of Day 1 by Jon Callas and my favorite quote
“Make your devices fixable”. Enough said.
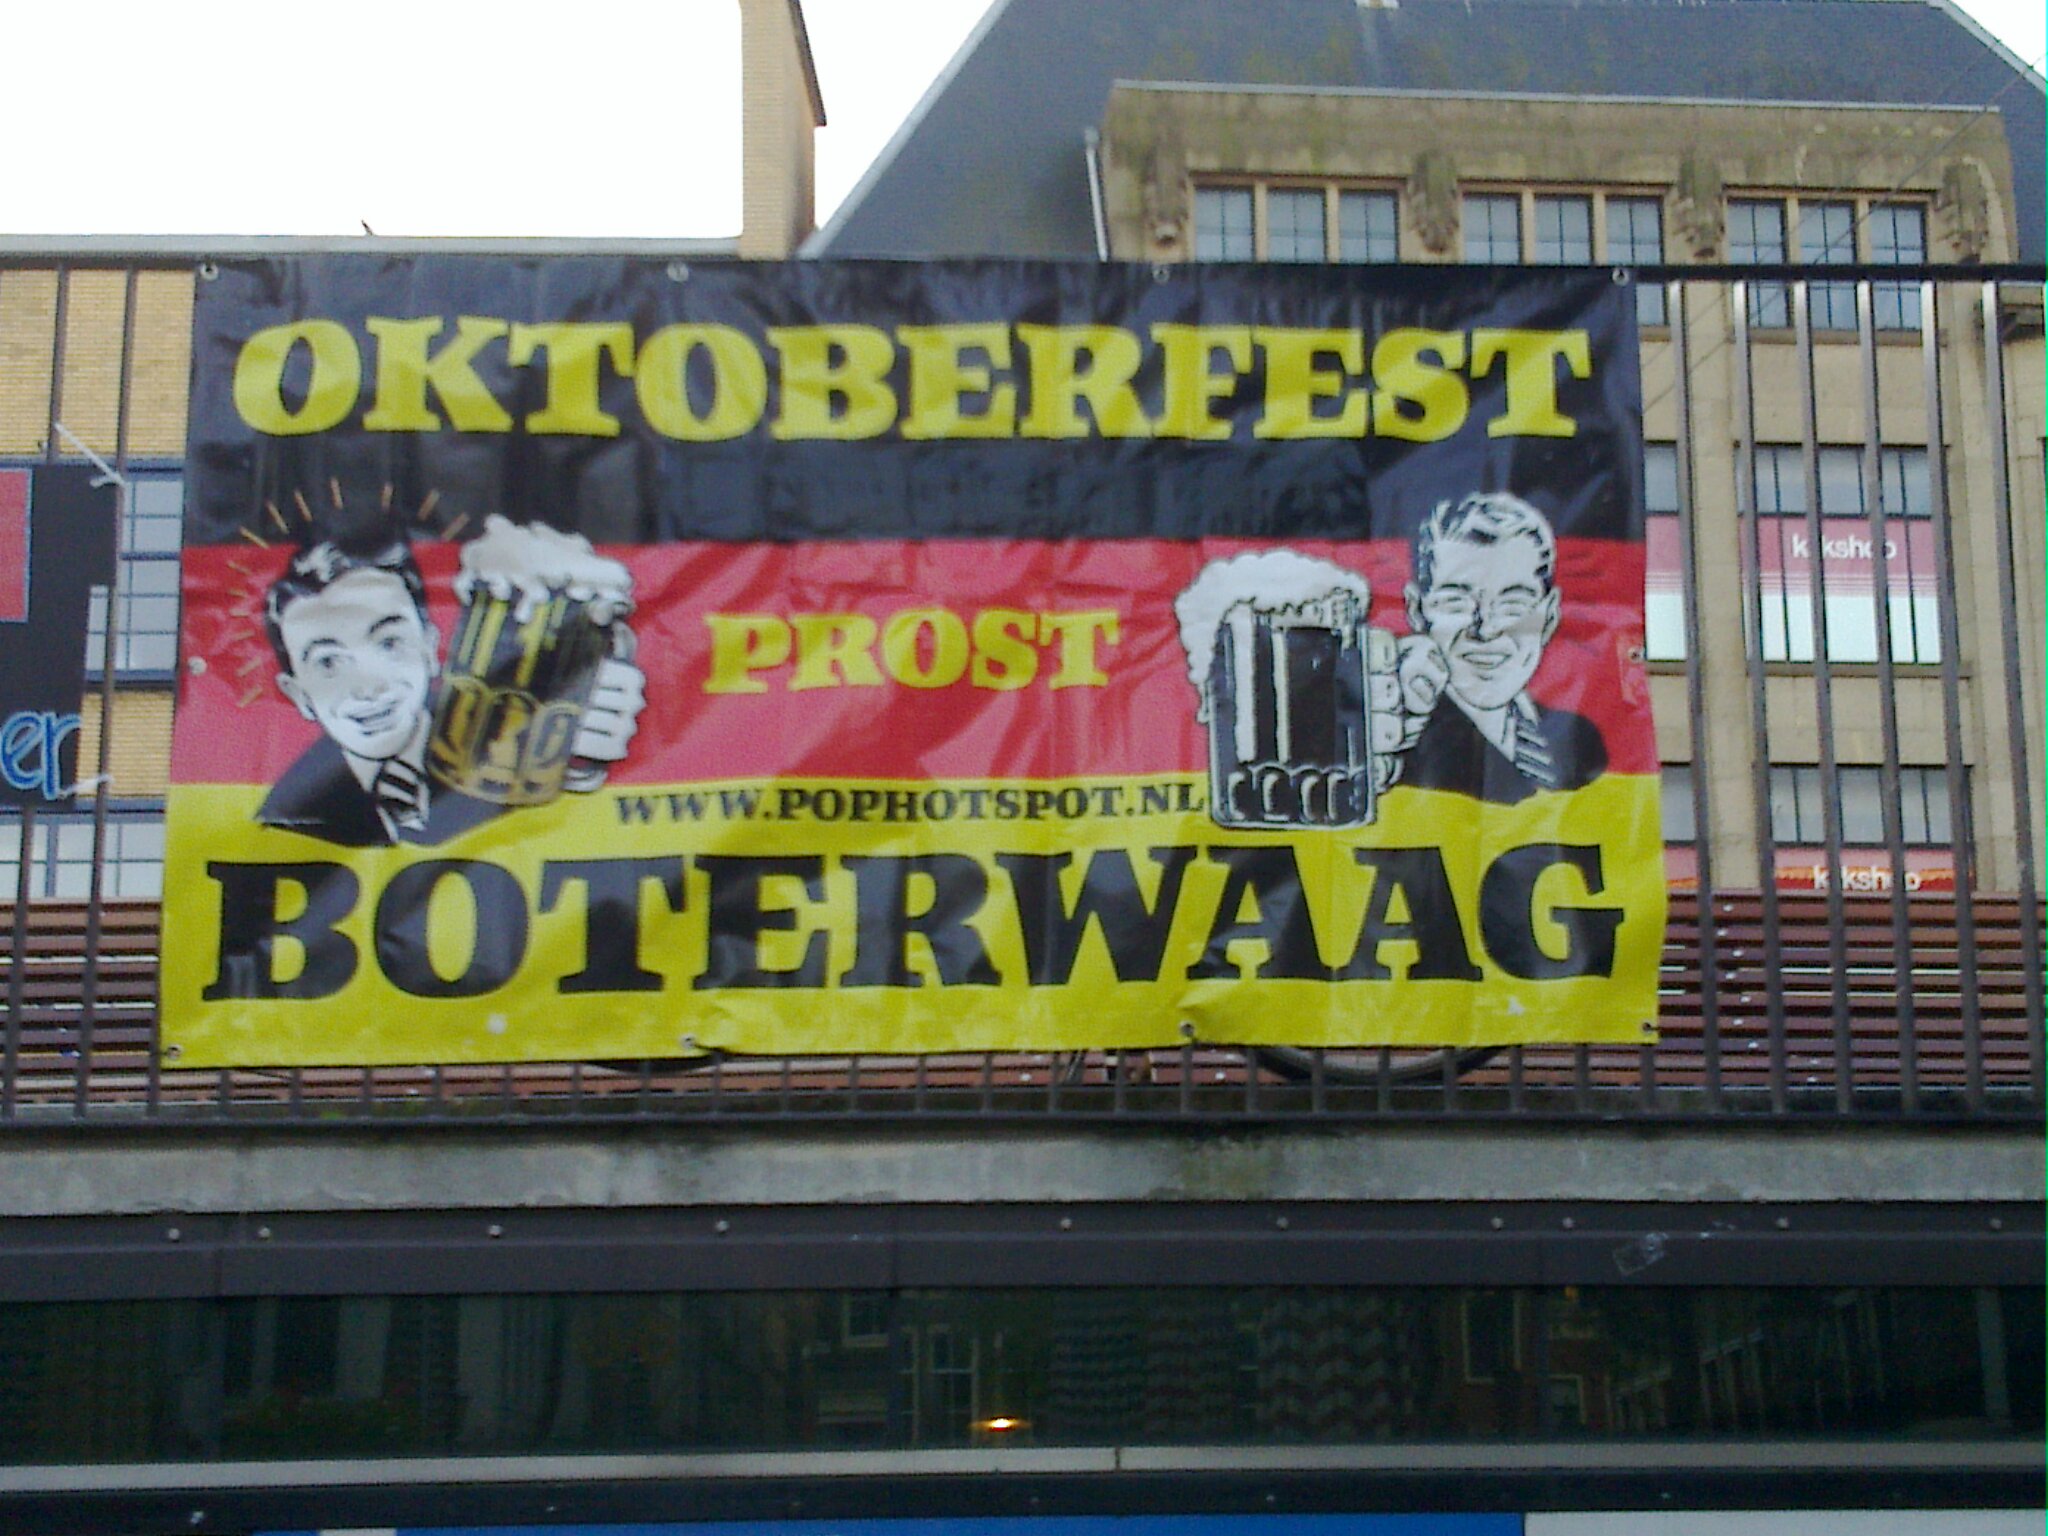
Unlike the German Oktoberfest in Munich which already started in September, the
Oktoberfest in The Hague started on 2nd October.
In spite of this competing event the decision going to the last day of the
hardwear.io Conference definitely paid off.
Day 2 started with the Keynote from Harald Welte (the father of Osmocom) and his
view about Telecom Security for the last few years. His observation is that
nothing has changed so far – we still suffer from a lack of tools and
monoculture throughout the industry.
On October 1st and 2nd Flo and I were presenting at
hardwear.io in The Hague, NL. My topic was
“Living in a fool’s wireless-secured paradise”
and Flo was presenting his current research
on medical device security. It was the first talk at an international
security conference for me and I am still quite excited!
I was speaking about the (in)security of wireless consumer alarm
systems, which you can buy just in every consumer electronics store
around the corner for about $10 – $250. I analyzed the systems on
different levels, e.g. looking at UART and JTAG and the wireless domain
with Software Defined Radio (SDR). I gave an overview of my current
research and the tools I usually use for hardware hacking, especially my
favorite thing to play with: SDR.