This blogpost contains summaries of talks from this year’s
TROOPERS18 Defense & Management Track.
All Your Cloud Are Belong to Us
The talk “All Your Cloud Belong Are Belong to Us” was held by
Nate Warfield, who is a Senior Security Program
Manager for the Microsoft Security Response Center (MSRC).
Before Microsoft he worked as a network engineer about 18 years and 10 of this
for a large amount of cell phone companies.
Nate gives an overview about the state of the cloud solution provided by
Microsoft, Azure, and how he hunts vulnerabilities in this environment.
Finally he concludes that the giving up your infrastructure to the cloud doesn’t
mean that you give up your responsibility.
In various scenarios it might be helpful or even required to have a statically
compiled version of Nmap available. This applies to e.g. scenarios where only
limited user privileges are available and installing anything to the system
might not be desirable.
For such cases I’ve started to create recipes to build such binaries. Similar
projects are already available on GitHub, but there are several reasons why I
chose to create my own tools:
A new ERNW whitepaper was just published. I wrote this whitepaper in the course
of my bachelor thesis and it examines multi-factor authentication in Microsoft
Windows environments:
Credential theft and the subsequent reuse of stolen credentials are a
significant problem in today’s information security. To counter the associated
risks, a planned approach is required as part of a comprehensive security
architecture program. This includes the implementation of multi-factor
authentication as an important building block. This whitepaper covers the
relevant steps of implementing a multi-factor authentication system in an
enterprise environment and closes with a security evaluation.
In this post we’ll take a detailed look at the properties of the Windows Server
2016 IPv6 stack.
I perform(ed) this exercise for several reasons:
Server 2016 is the latest OS released by Microsoft so this might give an
indication as for their plans & strategy when it comes to supporting certain
specifications.
(here you may keep in mind that the ~50 IETF meetings having passed since the
publication of RFC 2460 provided ample opportunity for creative minds to come
up with ever new ideas for “enhancing” IPv6, without too much real-life
feedback/reality checks from enterprise space though, as simply not many of
such organizations have deployed it at scale… or are incentivized to send
their employees to week-long meetings in expensive hotels on other continents
twice a year…).
as I laid out
in this post
the configuration approach an organization takes for their servers might
depend on the support of specific features.
obviously for both IPv6 planning and operations it might be helpful to
understand the respective behavior of individual operating systems (which is
why we researched stuff like
this
or
this
in the past).
many years ago Microsoft published white papers with details as for the TCP/IP
parameters of their OSs (incl. stuff like registry parameters to control it
etc.) but I’m not aware of such a document for Server 2016 or Windows 10. I
hence hope this post can somewhat contribute to public knowledge of the
intricacies of their latest IPv6 stack.
Last week, we decided to take a look onto the EMET library provided by
Microsoft. This library is intended to introduce several security features to
applications which are not explicitly compiled to use them.
It also adds an additional layer to protect against typical exploiting
techniques by filtering library calls, preventing usage of dangerous
functions/components and inserting mitigation technologies.
As EMET is already a target for many researchers, we currently only started to
get an overview of it’s structure and how the different components are
interacting with each other. Today we would like to share some of our results
with you.
In a recent assessment, we had to evaluate how Microsoft’s System Management
Server (SMS) certificate management solution (CMS) stores and handles
certificates. This question came up because sensitive, encrypted user
certificates were to be stored in the SMS CMS. Due to the sensitivity of the
handled certificates, we assessed the protection capabilities of the certificate
management solution against extraction attempts from a local attacker with
administrative privileges.
How did we do it?
We determined a five steps approach to gain access to the certificates and be
able to decrypt the accessed certificate material:
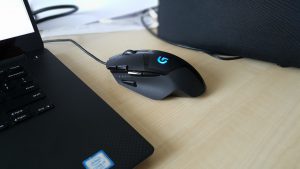
Ever got a backdoor installed on your computer by your beloved mouse? Here’s the
story of a poor mouse that got really, really sick.
Agent “Danger Mouse”
Do you remember the times where people put Teensy-boards and USB hubs in their
mouses? [Chris? ;)] Their aim was to attach an additional
Human Interface Device
(HID, like keyboards or mouses) with some payload in kind of e.g. keystrokes or
mouse movements. Also, there are devices available like the USB Rubber Ducky in
the housing of a USB thumb drive.
The principle is easy: The tools are using a programmable microcontroller with
the capability to emulate USB HID. That’s it. Just program your board of choice
with the payload fitting your needs and plug it in at the target computer. The
latter will recognize it as a keyboard/mouse and the payload-keystrokes will be
entered.
But why should external hardware be used? Many modern gaming peripherals provide
functions to store macros on them, including enough onboard memory for little
payloads.
Usually I’m not the kind of guy who talks about such economic topics. Because
I’m an engineer / security researcher who is exclusively concerned with
understanding technical problems and if possible, solving them accordingly. My
whole education is based on this and contains predominantly technical aspects of
information security. This sometimes makes it difficult to understand what the
market cares about (and why some products are being developed / exist on the
market 😉 ). Nevertheless, a current engagement for one of our customers made me
stumble upon such a product.
A
talk
about DirectAccess (an IPv6-only VPN solution) was given by our colleague Ali
Hardudi during IPv6 summit. Ali has recently finished his master thesis on this
topic.
The DirectAccess VPN technology was introduced by Microsoft starting from
Windows server 2008. It allows users remotely, seamlessly and securely connect
to their internal network resources without a need to provide user credentials,
which is done using different technologies such as Windows domain group
policies.
PowerView does not use the built in AD cmdlets to be independent from the Remote
Server Administration Tools (RSAT)-AD PowerShell Module which is only compatible
with PowerShell 3.0+ and by default only installed on servers that have Active
Directory services roles. PowerView, however, is compatible with PowerShell 2.0
and has no outer dependencies. Furthermore, it does not require any installation
process.