Currently there’s quite some discussion ongoing why it took Apple so long to fix a severe vulnerability in the update process of iTunes. A severe vulnerability which could easily be exploited by means of an automated tool called evilgrade which can be downloaded here (Hi Francisco!). Just one small note here: did you know that evilgrade was first shown and released at the 2008 edition of Troopers? We had a number of initial releases of tools in the last years (like wafw00f at the 2009 edition and VASTO at the 2010 edition) and we will continue this fine tradition in 2012. I can already promise that some nice code is going to be released for the first time at Troopers12…
Continue reading Continue readingCarriers Converge Their Internet and MPLS Infrastructure: Time to Redo Your Risk Assessment?
The above is the exact title of a Gartner research note published some days ago. Its main thesis is that an increased convergence of carriers’ MPLS and Internet infrastructures onto shared IP infrastructures requires that enterprises re-evaluate their security and performance risks.
While I do not agree with the overall line of reasoning in the paper, it still highlights a number of interesting points when it comes to MPLS security. Which in turn reminds me of quite some stuff we’ve done in the past, mainly our Black Hat Europe 2009 talk “All your packets are belong to us – Attacking backbone technologies”. Today we’ll release an updated version of the accompanying whitepaper as a kind-of technical report. Its title is “Practical Attacks against MPLS or Carrier Ethernet Networks” and it can be found here.
Continue reading Continue readingA Wrap-up on MFD Security
On last year’s TROOPERS11, Matthias (mluft) and I gave a talk on Multifunction Devices. Hardly surprising: It was related to the state of secure operation of MFDs. It was heavily motivated by experiences we collected out in the wild. We faced a frightening low level of awareness concerning the role of MFDs for the overall security picture – in particular regarding the processing of sensitive data…
However, instead of only showing and proving well-known weaknesses and vulnerabilities, we decided to adapt ERNW’s *Seven Sisters *model in order to match the needs of secure MFD operation and to develop some kind of guideline. As Matthias already lost some words on this, I’m not gonna waste your valuable time by repeating, what has already been said. However I described our approach and our thoughts on that topic in a recently published ERNW Newsletter. If for what ever reason you didn’t see our talk or even didn’t attend TROOPERS11 at all, have a look on Newsletter 37 and give us feedback on what you think about the whole topic…
Continue reading Continue readingCall me Snake
Once again there’s a reference to some action movie here, as some of you may have immediately spotted ;-).
For the record: this one is from “Snake Plissken”, the main protagonist in John Carpenter’s “Escape from New York”. There’s another well-known quote of the same character in the kind-of sequel “Escape from L.A.” which goes like: “The more things change, the more they stay the same”. I’m aware that this is not the initial source (but French novelist Jean-Baptiste Alphonse Karr presumably is, at the time in French ;-)); still this gives a nice transition to today’s topic.
Continue reading Continue reading“What’s so special about Troopers?”
This week I stayed some days in Zurich, to give a workshop and to meet both clients and fellow researchers (kudos again to C. for the awesome office tour @Google). In the course of one of those dinners somehow Troopers was mentioned and a guy asked: “I’ve heard of the conference. What’s so special about it?”
Funnily enough I didn’t even have to respond myself as a 2011 attendee coincidentally present at the table jumped in and started praising the event (“best con ever. great spirit, great talks”). Obviously this gave me a big grin… but it reminded as well me that some of you might ask themselves the very same question.
Continue reading Continue readingA Sneak Peek into TROOPERS12
 Here we go again: TROOPERS12 is scheduled for March 19^(th) – 23^(rd) 2012 in Heidelberg, Germany.
Those who attended TROOPERS before know for what we are up to. For all newcomers I’ll quickly outline what’s going to happen:
TROOPERS is your premium IT security event in Europe. Think of your usual IT educational event without annoying sales pitching and outdated topics. Now add a superb conference location, an elite line-up of international researchers and practitioners as well as an organizing team not dedicated to make a living doing this, but to celebrate our craftsmanship together with like-minded people.
Continue reading Continue readingiOS 5, S/MIME, and Digital Certificate Management
As a follow-up to this post somebody pointed us to this interesting article on S/MIME support and associated certificate mgmt in iOS 5. Nice read which some of you may find worthwhile.
On a related note: if anyone is aware of an easy way/good (3rd party) solution for pushing certs to iOS devices (besides SCEP) we would be very interested in that one. In that case pls leave a comment or shoot us an email.
Continue reading Continue readingShort iCloud Follow-Up
After the basic iCloud discussion in this post, I would like to add some more technical information. The following items are just a loose compilation of facts about the mentioned controls which allow the restriction of iCloud usage. The basic iCloud usage, consisting of backup, document sync, and photo stream, can be deactivated using the most recent version of the iPhone Configuration Utility:
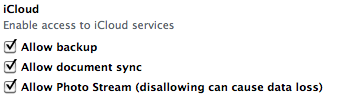
Since there are no default settings for these values, it is necessary to include the disabled entries in existing configuration profiles.
Continue reading Continue readingAll Your Clouds are Belong to us
This is a _very_ interesting paper just published by some researchers (mainly) from RUB (Ruhr-University Bochum). Here’s the abstract:
“Cloud Computing resources are handled through control interfaces. It is through these interfaces that the new machine images can be added, existing ones can be modied, and instances can be started or ceased. Effectively, a successful attack on a Cloud control interface grants the attacker a complete power over the victim’s account, with all the stored data included.
Continue reading Continue readingiTrust. Or not?
A few days ago (on 10/12/2011) Apple launched its new cloud offering which is called — who would have guessed 😉 — iCloud. Since we’re performing quite some research in the area of cloud security, we had a first look at the basic functionality and concepts of the iCloud. Its main features include the possibility to store full backups of Apple devices (at least, an iPhone, iPad or iPod touch running iOS 5 or a Mac running OS X Lion 10.7.2 is required), photos, music, or documents online. The data to be stored online is initially pushed to the cloud storage and then synchronized to any device which is using the same iCloud account. From this moment on, all changes on the cloudified data is immediately synchronized to the iCloud and then pushed to all participating devices. At this point, most infosec people might start to be worried a little bit: The common cloud concept of centralized data storage on premise of a third party does not cope well with the usual control focused approach of most technical infosec guys. The resulting concerns can be attributed to several main cloud computing related risks (which are proposed by ENISA and actually very valuable work:
Continue reading Continue reading