As we historically have a strong connection to network technologies (not
surprising, given the “NW” in “ERNW” stands for “Networks”), I developed a small
script to create RFC-style ASCII representations of protocol schemes. The
following listing shows an example created for a fictitious protocol:
A few weeks ago I gave a presentation with the above title at some corporate
infosec event. Given I’ve been asked for the slides many times now, I’ve
converted them to a PDF which can be found
here.
We hope to contribute to the necessary debate thereby…
Reading
this article from
the Guardian, on this guy apparently being
banned from fully discussing research results in
his talk
at upcoming
USENIX Security, leaves me
scratching my head once more. Things might (as so often) be more complex than
they seem, but this looks like yet-another misconception as for the contribution
of security research (and its public discussion) to the greater good of us all.
Which is unfortunate for the speakers (I’ve been in a similar situation once,
receiving a threatening legal letter from a very large organization one day
before one of our Black Hat presentations and can tell you that stuff like that
doesn’t add to one’s anticipation of the talk or the event…), for the audience
(including some ERNW guys who will be a USENIX-SEC, so, btw, expect a summary
post here) and for the whole community of security researchers.
“Nein! Ein von unbeugsamen Galliern bevölkertes Dorf hört nicht auf, dem
Eindringling Widerstand zu leisten.”
This is a famous quote pretty much every German kid used to know. Not sure if
this still applies though, my three haven’t touched Asterix comics so far.
Anyhow, you might ask why I cite this.
Simple answer: see
this recent article
from the Guardian on a Utah-based ISP “resisting some pressure”. That’s the
spirit…
Some days ago a security advisory related to web application firewalls (WAFs)
was published on Full Disclosure. Wendel Guglielmetti Henrique found another bug
in the IBM Web Application Firewall which can be used to circumvent the WAF and
execute typical web application attacks like SQL injection (click
here
for details). Wendel talked already (look
here)
at the Troopers Conference in 2009 about the different
techniques to identify and bypass WAFs, so this kind of bypass methods are not
quite new.
On Friday we released our latest technical newsletter with the fancy title
“Sell Your Own Device – A Field Study on Decommissioning of Mobile
Devices”. It is the result of a field study on decommissioned mobile business
devices bought on eBay and about how stored data may be extracted in different
ways.
As always we love to share plenty of practical advise: At the end of the
newsletter you will find the mitigating controls to securely handle mobile
devices at the end of their life cycle process.
Currently there’s
quite some discussion
ongoing why it took Apple so long to fix a
severe vulnerability in the update process
of iTunes. A severe vulnerability which could easily be exploited by means of an
automated tool called
evilgrade which can
be downloaded here (Hi
Francisco!). Just one small note here: did you know that evilgrade was first
shown and released at the 2008 edition of
Troopers? We had a number of initial releases of tools
in the last years (like
wafw00f at the
2009 edition and
VASTO at the
2010 edition) and we will
continue this fine tradition in 2012. I can already promise that some nice code
is going to be released for the first time at Troopers12…
Once again there’s a
reference to
some action movie here, as some of you may have immediately spotted ;-).
For the record: this one is from “Snake Plissken”, the main protagonist in John
Carpenter’s “Escape from New York”. There’s another well-known quote of the same
character in the kind-of sequel “Escape from L.A.” which goes like: “The more
things change, the more they stay the same”. I’m aware that this is not the
initial source (but French novelist Jean-Baptiste Alphonse Karr presumably is,
at the time in French ;-)); still this gives a nice transition to today’s
topic.
This week I stayed some days in Zurich, to give a workshop and to meet both
clients and fellow researchers (kudos again to C. for the awesome office tour
@Google). In the course of one of those dinners somehow Troopers was mentioned
and a guy asked: “I’ve heard of the conference. What’s so special about it?”
Funnily enough I didn’t even have to respond myself as a
2011 attendee
coincidentally present at the table jumped in and started praising the event
(“best con ever. great spirit, great talks”). Obviously this gave me a big grin…
but it reminded as well me that some of you might ask themselves the very same
question.
After the basic iCloud discussion in
this post, I would like to
add some more technical information. The following items are just a loose
compilation of facts about the mentioned controls which allow the restriction of
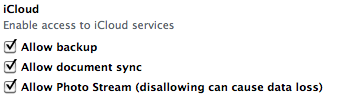
iCloud usage. The basic iCloud usage, consisting of backup, document sync, and
photo stream, can be deactivated using the most recent version of the
iPhone Configuration Utility:
Since there are no default settings for these values, it is necessary to include
the disabled entries in existing configuration profiles.