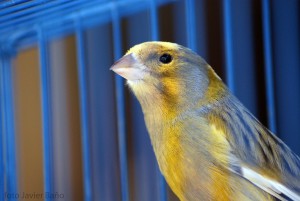
Well, it’s a canary (these cute yellow songbirds some people have as a pet), and
its main feature is that it dies before you will.
What the hack [pun intended]? And by the way… what has this to do with IT
Security? Well… let me first quote Wikipedia on the birds:
“Canaries were once regularly used in coal mining as an early warning system.
Toxic gases such as carbon monoxide, methane or carbon dioxide in the mine
would kill the bird before affecting the miners. Signs of distress from the
bird indicated to the miners that conditions were unsafe.”
Source: https://en.wikipedia.org/wiki/Domestic_canary#Miner.27s_canary
I wrote a small python script that extracts the content from Alcatel .tim
firmware files. It took some time staring at hex values, as well as a fair
amount of guess work to figure out the file format.
All .tim files start with a common header, containing the TiMOS version string,
the build string, the used compression algorithm and the number of segments
included in the file. The common header is followed by a header for each segment
in the file. The segment header contains values like the name of the segment,
the beginning of the segment in the image file, the size of the segment,
compressed as well as extracted, a checksum of the decompressed data and also
the base address and entry point of the data in the routers memory. A segment
header can look like this:
There has been, again, some development within the loki domain. Today I’m going
to write about the latest module added to the suite, a module for decoding and
cracking Cisco’s TACACS+.
TACACS is the Terminal Access Controller Access-Control System, a protocol for
handling remote user authentication and central access control. It originated in
1984 and was used in the old Unix world. TACACS+ is a related protocol developed
by Cisco Systems and is widely used for AAA (Authentication, Authorization,
Accounting) on IOS based devices. It was released as an
open standard in 1993 (and
expired in 1998 by the way ;-)).
On March 16^(th), 2015, at the Troopers
IPv6 Security Summit,
we finally released the SI6 Networks’ IPv6 Toolkit v2.0 (Guille). The
aforementioned release is now available at the
SI6 IPv6 Toolkit homepage. It is
the result of over a year of work, and includes improvements in the following
areas:
Increased portability
Bug fixes
Additional features in existing tools
Brand-new tools
Increased Portability
One of the goals that the SI6 Toolkit had since its inception is that of
portability. The SI6 Toolkit has supported all major BSD-derived OSes, Linux,
and Mac OS for a number of years now. And this new release supports yet another
new platform: OpenSolaris. We believe that besides supporting a greater user
base, increased portability ultimately results in improved code quality.
Lately we had to analyze QR-Codes in a pentest. Those held some random data
which was used as a token for login and we wanted to know if that data was
really random.
If you ever worked with the Burp Suite you may know the Burp Sequencer, which
offers some statistical analysis regarding the randomness of tokens which appear
in requests (you just have to tell Burp what or where the token is). In our case
the QR-Code was delivered as an inline-image in HTML to the browser, like this:
Last week I had the pleasure to give you my impressions regarding my experience
about
hacking for b33r at Ghent,
that is, my participation at BruCON 2014 hacking
conference. As I said among else, the reason that I was there was to present
Chiron, my IPv6 penetration
testing/security assessment framework, which was supported by the
Brucon 5×5
program. The first version of Chiron had been presented at
Troopers 14,
during the
IPv6 Security Summit.
As we continue our research in the 3GPP protocol world, there is a new tool for
you to play with. It is called s1ap_enum and thats also what it does 😉
The tool itself is written in erlang, as i found no other free ASN.1 parser that
is able to parse those fancy 3GPP protocol specs. It connects to an MME on
sctp/36412 and tries to initiate a S1AP session by sending an S1SetupRequest
PDU. To establish a S1AP session with an MME the right MCC and MNC are needed in
the PLMNIdentity. The tool tries to guess the right MCC/MNC combinations. It
comes with a preset of known MCC/MNC pairs from
mcc-mnc.com, but can try all other combinations as
well.
As we historically have a strong connection to network technologies (not
surprising, given the “NW” in “ERNW” stands for “Networks”), I developed a small
script to create RFC-style ASCII representations of protocol schemes. The
following listing shows an example created for a fictitious protocol:
Having just finished the second
“Advanced Attack Techniques against IPv6 Networks” workshop (some
of the course material can be found
here),
organised and hosted by ERNW and their partner
HM Training Solutions, I would like to
take this opportunity to release publicly one of my scripting tools, an IPv6
scanner. This tool is based on Scapy (so you have to install Scapy and its
prerequisites before using it). It should not be considered as a replacement or
a competitor of nmap against IPv6 or of the scanners incorporated into the great
IPv6 toolkits already released by Marc Heuse
and Fernando Gont,
but, instead, as a tool released mainly for educational purposes. Specifically,
this scanner, apart from supporting some of the most well known port scanning
techniques, from ping scanning to SYN, RESET, ACK, XMAS, etc., etc., TCP or UDP
scanning, it also combines, by using the suitable switches, some IDS/IPS evasion
techniques. As I have found out up to now, at least two of them, if used
“properly”, can be effective against a very popular IDS/IPS software used by
many “Fortune 100” companies out there. This means that you can launch actually
any type of the supported network-scanning techniques while flying under the
radar of this specific IDS software (and perhaps some other too, who knows…).
But first of all, as always please check the corresponding README file.
Its been a long time, since i released the last version of pytacle, but now the
time has come. Here is alpha2 with some new features:
– Support of RTLSDR sticks
– Possibility to scan for cells around you
– Changed the code to generate real KCs (but as nobody noticed the wrong KCs i
guess you were good with the others 😉
Im also planning to address hopping channels in the future, but ive not made it
far enough in my DSP lecture, yet 😉