We’re delighted to provide the first announcement of talks of next year’s
Troopers edition. Looks like it’s going to be a
great event again
.
Here we go:
Jacob Torrey – The foundation is rotting and the basement is flooding: A deeper
look at the implicit trust relationships in your organization FIRST
TIME MATERIAL
Synopsis: In this session, a new hardware-level attack on PCIe is presented as
an example for the implicit trust your organization places in 3rd parties. These
implicit trust relationships that are typically overlooked will be closely
examined under the lens of “InfoSec debt” and providing guidance to InfoSec
decision makers on the ROI or risks of adding additional IT services/appliances
to an organization’s network.
The “InfoSec debt” metric can then be tracked over time and provides an
intuitive way to explain the cost/benefits of IT security to other
organizational stakeholders.
TROOPERS14 has come to an end, and it’s finally time to let you have a go at the
Badge’s source code. As promised, it was slightly modified and extended, to show
you the full potential of your new gadget. I’ve added some nice payloads from
Nikhil Mittal and a few own ones. Above that, for those who took their parts for
soldering home, I’ve also added a few quick instructions on how to do the
soldering.
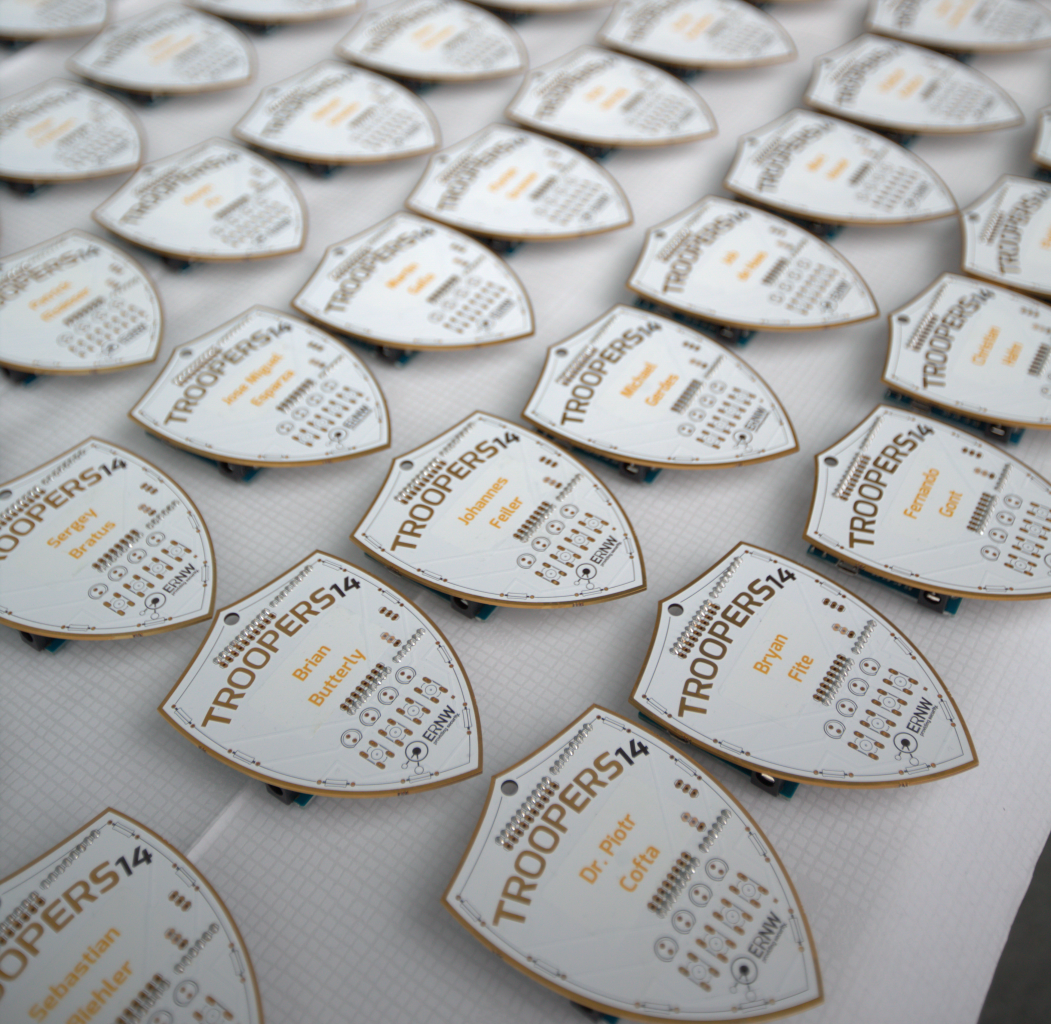
Greetings from the Print Media Academy in Heidelberg. Just in time for
TROOPERS14, I’ve got the great honor to present this years badge!
Being a TROOPER is tough: You need to know loads of information, learn even more
and be able to work fast.
This year we decided to increase your efficiency and speed when collecting data
from computer systems and, let’s say, hacking them! Your newest gadget is based
on a plain
Arduino Leonardo,
modded with one of our famous shields. After adding a few LEDs and buttons, it
will power up to full functionality.
This is a guest post from Vladimir Wolstencroft from our friends of
aura information security
==================================================================
Mobile messaging applications have been occupying people’s attention and
it seems to be all the latest news. Perhaps I should have called my presentation
the 19 Billion dollar app but at the time of writing and research I thought the
proposed 3 Billion dollar amount for SnapChat was a little ludicrous, who could
have known that would have been just a drop in the ocean.
Given we’ve received a number of inquiries as for the agenda of this year’s
TelcoSecDay here’s a first preliminary agenda. To get an idea of the event’s
character you might have a look at the agenda of the
2012 edition
or the
2013 edition.
Pls note that there might be changes/additions to the following outline as we’re
currently discussing potential contributions with two European operators. Here
we go, for today:
9:00: Opening Remarks & Introduction
9:15: Ravi Borgaonkor – Evolution of SIM Card Security
10:15: Break
10:45: Adrian Dabrowski
11:45: Collin Mulliner – PatchDroid – Third Party Security Patches for Android
12:30: Lunch
13:45: Philippe Langlois
14:45: Break
15:15: Haya Shulman – The Illusion of Challenge-Response Authentication
16:00: Christian Sielaff & Daniel Hauenstein – Breaking Network Monitoring Tools
Used in Telco Space
16:30: Closing Remarks
19:00: Joint dinner (hosted by ERNW) in Heidelberg Altstadt for those interested
and/or staying for the main conference
Today we have to pleasure to announce another round of
Troopers talks.
Here we go:
Noam Liram: Vulnerability Classification in the SaaS Era FIRST TIME
MATERIAL
Abstract: In this talk we will thoroughly analyze two major SaaS vulnerabilities
that were found by Adallom (one of which is still in responsible disclosure
stages at the time of writing). By demonstrating this new class of exploits
which we have nick-named “Ice Dagger” attacks, we aim to change the current
industry-wide criteria for vulnerability classifications, which were developed
in the Desktop/Server world, are inadequate when classifying SaaS
vulnerabilities. We will specifically discuss the details of MS13-104.
At first a very happy new year to all our readers!
Today we announce the third round of Troopers 2014 talks (first round
here,
second
here).
Here we go:
===
Daniel Mende: Implementing an USB Host Driver Fuzzer FIRST TIME
MATERIAL
Abstract: The Universal Serial Bus (USB) can be found everywhere these days, may
it be to connect a mouse or keyboard to the computer, transfer data on a flash
drive connected via USB or to attach some additional hardware like a Digital
Video Broadcast receiver. Some of these devices use a standardized device class
which are served by an operating system default driver while other, special
purpose devices, do not fit into any of those classes, so vendors ship their own
drivers. As every vendor specific USB driver installed on a system adds
additional attack surface, there needs to be some method to evaluate the
stability and the security of those vendor proprietary drivers. The simplest way
to perform a stability analysis of closed source products is the fuzzing
approach. As there have been no publicly available tools for performing USB host
driver fuzzing, I decided to develop one ;-), building on Sergey’s and Travis’
legendary
Troopers13 talk.
Be prepared to learn a lot about USB specifics, and to see quite a number of
blue screens and stack traces on major server operating systems…
We’re very happy to announce the second round of Troopers 2014 talks today
(first round
here).
Some
(well, actually most 😉 ) of these talks haven’t been presented before, at any
other occasion, so this is exciting fresh material which was/is prepared
especially for Troopers.
Andreas Wiegenstein & Xu Jia: Risks in Hosted SAP Environments.FIRST TIME
MATERIAL
**Synopsis: **Many SAP customers have outsourced the operation of their SAP
systems in order to save cost. In doing so, they entrust their most critical
data to a hosting provider, potentially sharing the same SAP server with a
number of companies and organizations unknown to them. These companies and
organizations virtually sit in the same boat, without knowing each other and
without trusting each other. They all trust in the ability of their hosting
provider to run their operating environment in a secure way, though.
We’re delighted to provide the first announcement of talks of next year’s
Troopers edition. Looks like it’s going to be a great
event again 😉
Here we go:
==================
Toby Kohlenberg: Granular Trust – Making it Work
Over the last 5 years the concept of using dynamic or granular trust models to
control access to systems, networks and applications has become well known and
is now seeing partial adoption in many places. The challenge is how granular and
dynamic can you get and the question is whether it is worth it. As the architect
of Intel’s trust model Toby can speak to the entire journey from initial idea
through current implementation and the likely road ahead. This talk will include
the good, bad and ugly parts of designing a trust model and then implementing it
in a Fortune 50 company’s production environment. You will learn from his
mistakes so you can make different ones.
 .