On Friday we released our latest technical newsletter with the fancy title
“Sell Your Own Device – A Field Study on Decommissioning of Mobile
Devices”. It is the result of a field study on decommissioned mobile business
devices bought on eBay and about how stored data may be extracted in different
ways.
As always we love to share plenty of practical advise: At the end of the
newsletter you will find the mitigating controls to securely handle mobile
devices at the end of their life cycle process.
This is a guest post by the SAP security experts of BIZEC. Enjoy reading:
On March 20^(th), the first BIZEC workshop will be held
at the amazing Troopers conference in Heidelberg, Germany. For those still
unfamiliar with BIZEC: the business application security initiative is a
non-profit organization focused on security threats affecting ERP systems and
business-critical infrastructures.
The main goals of BIZEC are:
Raise awareness, demonstrating that ERP security must be analyzed
holistically.
Analyze current and future threats affecting these systems.
Serve as a unique central point of knowledge and reference in this subject.
Provide experienced feedback to global organizations, helping them to increase
the security of their business-critical information.
Organize events with the community to share and exchange information.
The
“BIZEC workshop at Troopers 2012”
will dive into the security of SAP platforms. Still to this day, a big part of
the Auditing and Information Security industries believe that Segregation of
Duties (SoD) controls are enough to protect these business-critical systems.
By attending this session, InfoSec professionals and SAP security managers will
be able to stop “flying blind” with regards to the security of their SAP
systems. They will learn why SoD controls are not enough, which current threats
exist that could be exploited by evil hackers, and how to protect their
business-critical information from cyber-attacks.
About
two months ago the Bluetooth SIG
renamed their latest standard,
which was previously known as “Bluetooth v4.0”. When version numbers get higher
and higher marketing likes to interfere and try something new. In this case:
Bluetooth Smart.
Sounds smart, but is it?
Without getting into too much detail, let me quickly quote Wikipedia to get
started:
“Cost-reduced single-mode chips, which enable highly integrated and
compact devices, feature a lightweight Link Layer providing
ultra-low power idle mode operation, simple device discovery, and
reliable point-to-multipoint data transfer with advanced power-save
and secure encrypted connections at the lowest possible cost.”
Here we go again: TROOPERS12 is scheduled for March 19^(th) – 23^(rd) 2012 in Heidelberg, Germany.
Those who attended TROOPERS before know for what we are up to. For all
newcomers I’ll quickly outline what’s going to happen:
TROOPERS is your premium IT security event in Europe. Think of your usual IT
educational event without annoying sales pitching and outdated topics. Now add a
superb conference location, an elite line-up of international
researchers and practitioners as well as an
organizing team not dedicated to make a living
doing this, but to celebrate our craftsmanship together with like-minded people.
TROOPERS11 was a blast! We received great feedback from all attendees and
speakers. This really pushes ourselves towards the next goals and an even better
security conference in 2012.
We’re happy that everybody got home safely with new ideas and inspirations in
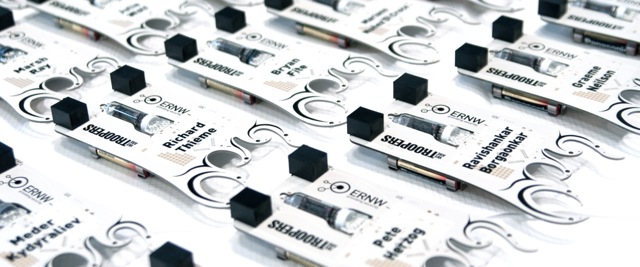
mind. On a side note: The awesome TROOPERS badge caused trouble for some of
you with the airport security 😉 I really hope everybody could find a way to
take it back home. It will hopefully find its way to an adequate place right
next to your old memorabilia (cup of the first won soccer match, your college
degree or photos from your first ballet show). Regard it as the proof of your
latest achievement and tell everybody proud and loud: WE ARE TROOPERS.
Just wanted to let you know that we sent out
ERNW Newsletter 32
end of last week. As we
promised
it includes the results of research regarding the question “Is browser
virtualization a valid security control in order to mitigate browser based
security risks?”.
Simon did a great job with writing the latest newsletter. It’s a 30-page
document which should help you to have a basis for well-informed decisions when
it comes to the deployment of an application virtualization technology.
Everybody who is interested in our newest tool ‘Loki’ is welcomed to head over
to ERNW’s tool section and
download it. Take this monster for a spin and let us know in the comments how
you like it. Loki’s coding father Daniel is more than happy to answer your
questions and criticism.
You don’t even know what Loki is?
In short: An advanced security testing tool for layer 3 protocols.
Yesterday we made our way to Vienna to participate and contribute to NinjaCon
(formerly known as PlumberCon, before Nintendo Inc. claimed their rights ;)).
After our arrival Oliver held a five hour workshop on
Penetration Testing and did the finishing
touches on his slides about
‘Attacking Cisco Enterprise WLANs‘, which
he will deliver later today together with Daniel. And last but not least Daniel
will be the Packet Master of PacketWars™ Vienna taking place in the evening.
I’m happy to announce that the presentations and a majority of the videos from
TROOPERS10 are finally available to you.
You’ll find the slides at the conference’s website
troopers.de, more precisely
here. Plenty of videos
were uploaded and are now ready for streaming at
viddler.com/TROOPERS. Enjoy!
Please excuse the long waiting time – this is a big point on our ‘improvements
for upcoming events’ list. Talking about improvements: If you have any
suggestions, criticism or even praise for past or upcoming events – let us know
in the comment section.
 About
two months ago the Bluetooth SIG
 Here we go again: TROOPERS12 is scheduled for March 19^(th) – 23^(rd) 2012 in Heidelberg, Germany.

